

[Dec 29, 2024] Get New SPLK-1002 Certification – Valid Exam Dumps Questions
100% Passing Guarantee - Brilliant SPLK-1002 Exam Questions PDF
Splunk SPLK-1002 exam is an online, proctored exam that consists of 60 multiple-choice questions. Candidates have 90 minutes to complete the exam, and they must achieve a passing score of 70% or higher. SPLK-1002 exam can be taken at any time, and candidates can schedule the exam according to their availability.
NEW QUESTION # 149
Information needed to create a GET workflow action includes which of the following? (select all that apply.)
- A. A label that will appear in the Event Action menu at search time.
- B. A URI where the user will be directed at search time.
- C. A name of the workflow action
- D. A name for the URI where the user will be directed at search time.
Answer: A,B,C
Explanation:
Reference: https://docs.splunk.com/Documentation/Splunk/8.0.3/Knowledge/SetupaGETworkflowaction
NEW QUESTION # 150
What are search macros?
- A. Reusable pieces of search processing language.
- B. A method to normalize fields.
- C. Categories of search results.
- D. Lookup definitions in lookup tables.
Answer: A
Explanation:
The correct answer isB. Reusable pieces of search processing language.
The explanation is as follows:
Search macros are knowledge objects that allow you to insert chunks of SPL into other searches12.
Search macros can be any part of a search, such as an eval statement or a search term, and do not need to
be a complete command12.
You can also specify whether the macro field takes any arguments and define validation expressions for
them12.
Search macros can help you make your SPL searches shorter and easier to understand3.
To use a search macro in a search string, you need to put a backtick character () before and after the
macro name[^1^][1]. For example,mymacro`.
NEW QUESTION # 151
When using a field value variable with a Workflow Action, which punctuation mark will escape the data
- A. *
- B. !
- C. ^
- D. #
Answer: B
Explanation:
When using a field value variable with a Workflow Action, the exclamation mark (!) will escape the data. A
Workflow Action is a custom action that performs a task when you click on a field value in your search
results. A Workflow Action can be configured with various options, such as label name, base URL, URI
parameters, post arguments, app context, etc. A field value variable is a placeholder for the field value that will
be used to replace the variable in the URL or post argument of the Workflow Action. A field value variable is
written as fieldname, where field_name is the name of the field whose value will be used. However, if the field
value contains special characters that need to be escaped, such as spaces, commas, etc., you can use the
exclamation mark (!) before and after the field value variable to escape the data. For example, if you have a
field value variable host, you can write it as !$host! to escape any special characters in the host field value.
Therefore, option B is the correct answer.
NEW QUESTION # 152
Which of the following is the correct way to use the datamodelcommand to search fields in the Webdata model within the Webdataset?
- A. datamodel=Web | search Web | fields Web*
- B. | search datamodel Web Web | fields Web*
- C. | datamodel Web Web search | fields Web*
- D. | datamodel Web Web fields | search Web*
Answer: B
NEW QUESTION # 153
Which of the following statements describe calculated fields? (select all that apply)
- A. Calculated fields can only be applied to host and sourcetype.
- B. Calculated fields are shortcuts for performing calculations using the eval command.
- C. Calculated fields can be based on an extracted field.
- D. Calculated fields can be used in the search bar.
Answer: B,C
NEW QUESTION # 154
When can a pipe follow a macro?
- A. The current user must own the macro.
- B. The macro must be defined in the current app.
- C. Only when sharing is set to global for the macro.
- D. A pipe may always follow a macro.
Answer: D
Explanation:
A macro is a way to save a segment of a search string as a variable and reuse it in other searches2. A macro
can be followed by a pipe, which is a symbol that separates commands in a search pipeline2. A pipe may
always follow a macro, regardless of who owns the macro, where the macro is defined or how the macro is
shared2. For example, if you have a macro called us_sales that returns events from the US region, you can use
it in a search like this: us_sales | stats sum(price) by product2. This search will use the macro to filter the
events and then calculate the total price for each product2. Therefore, option A is correct, while options B, C
and D are incorrect because they are not conditions that affect whether a pipe can follow a macro.
NEW QUESTION # 155
What does the following search do?
- A. Creates a table with the count of all types of corndogs eaten split by user.
- B. Creates a table of the total count of mysterymeat corndogs split by user.
- C. Creates a table of the total count of users and split by corndogs.
- D. Creates a table that groups the total number of users by vegetarian corndogs.
Answer: B
Explanation:
Explanation
The search string below creates a table of the total count of mysterymeat corndogs split by user.
| stats count by user | where corndog=mysterymeat
The search string does the following:
It uses the stats command to calculate the count of events for each value of the user field. The stats command creates a table with two columns: user and count.
It uses the where command to filter the results by the value of the corndog field. The where command only keeps the rows where corndog equals mysterymeat.
Therefore, the search string creates a table of the total count of mysterymeat corndogs split by user.
NEW QUESTION # 156
How many ways are there to access the Field Extractor Utility?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: C
NEW QUESTION # 157
Which field will be used to populate the field if the productName and product:d fields have values for a given event?
| eval productINFO=coalesco(productName,productid)
- A. The value for the productName field because it appears first.
- B. Neither field value will be used and the field will be assigned a NULL value for the given event.
- C. Both field values will be used and the product INFO field will become a multivalue field for the given event.
- D. The value for the field because it appears second.
Answer: A
Explanation:
The correct answer is B. The value for the productName field because it appears first.
The coalesce function is an eval function that takes an arbitrary number of arguments and returns the first value that is not null. A null value means that the field has no value at all, while an empty value means that the field has a value, but it is "" or zero-length1.
The coalesce function can be used to combine fields that have different names but represent the same data, such as IP address or user name. The coalesce function can also be used to rename fields for clarity or convenience2.
The syntax for the coalesce function is:
coalesce(<field1>,<field2>,...)
The coalesce function will return the value of the first field that is not null in the argument list. If all fields are null, the coalesce function will return null.
For example, if you have a set of events where the IP address is extracted to either clientip or ipaddress, you can use the coalesce function to define a new field called ip, that takes the value of either clientip or ipaddress, depending on which is not null:
| eval ip=coalesce(clientip,ipaddress)
In your example, you have a set of events where the product name is extracted to either productName or productid, and you use the coalesce function to define a new field called productINFO, that takes the value of either productName or productid, depending on which is not null:
| eval productINFO=coalesce(productName,productid)
If both productName and productid fields have values for a given event, the coalesce function will return the value of the productName field because it appears first in the argument list. The productid field will be ignored by the coalesce function.
Therefore, the value for the productName field will be used to populate the productINFO field if both fields have values for a given event.
References:
* Search Command> Coalesce
* USAGE OF SPLUNK EVAL FUNCTION : COALESCE
NEW QUESTION # 158
Which one of the following statements about the search command is true?
- A. It does not allow the use of wildcards.
- B. It behaves exactly like search strings before the first pipe.
- C. It treats field values in a case-sensitive manner.
- D. It can only be used at the beginning of the search pipeline.
Answer: B
Explanation:
Reference:https://docs.splunk.com/Documentation/SplunkCloud/8.0.2003/Search/Usethesearchcommand
NEW QUESTION # 159
What does the fillnull command replace null values with, it the value argument is not specified?
- A. NULL
- B. NaN
- C. N/A
- D. 0
Answer: D
NEW QUESTION # 160
Which of the following data models are included in the Splunk Common Information Model (CIM) add-on?
(select all that apply)
- A. Databases
- B. Alerts
- C. Email
- D. User permissions
Answer: A,B,C
Explanation:
The Splunk Common Information Model (CIM) add-on contains a collection of preconfigured data models
that you can apply to your data at search time. Each data model in the CIM consists of a set of field names and
tags that define the least common denominator of a domain of interest. The CIM currently has data models
defined for 22 categories, including Alerts, Databases, and Email. User permissions is not one of the
categories in the CIM.ReferencesSee Overview of the Splunk Common Information Model and Splunk
Common Information Model - Your Questions Answered.
NEW QUESTION # 161
Which function should you use with the transaction command to set the maximum total time between the
earliest and latest events returned?
- A. maxpause
- B. maxduration
- C. maxspan
- D. endswith
Answer: C
NEW QUESTION # 162
Where are the results of eval commands stored?
- A. In a database.
- B. In an index.
- C. In a field.
- D. In a KV Store.
Answer: C
Explanation:
https://docs.splunk.com/Documentation/Splunk/8.0.2/SearchReference/Eval The eval command calculates an expression and puts the resulting value into a search results field.
If the field name that you specify does not match a field in the output, a new field is added to the search results.
If the field name that you specify matches a field name that already exists in the search results, the results of the eval expression overwrite the values in that field.
NEW QUESTION # 163
Which one of the following statements about the search command is true?
- A. It does not allow the use of wildcards.
- B. It behaves exactly like search strings before the first pipe.
- C. It treats field values in a case-sensitive manner.
- D. It can only be used at the beginning of the search pipeline.
Answer: B
NEW QUESTION # 164
A user runs the following search:
index-X sourcetype=Y I chart count (domain) as count, sum (price) as sum by product, action usenull=f useother-f Which of the following table headers match the order this command creates?
- A. The chart command does not allow for multiple statistical functions.
- B. Count: product, sum: product, count: action, sum: action
- C. Product, sum: addtocart, sum: remove, sum: purchase, count: addtocart, count: remove, count: purchase
- D. Product, count: addtocart, count: remove, count: purchase, sum: addtocart, sum: remove, sum: purchase
Answer: D
Explanation:
The correct answer is C. Product, count: addtocart, count: remove, count: purchase, sum: addtocart, sum: remove, sum: purchase1.
In Splunk, the chart command is used to create a table or a chart visualization from your data2. The chart command takes at least one function and one field, and optionally another field to group by2.
In the given search, the chart command is used with two functions (count and sum), two fields (domain and price), and two fields to group by (product and action). The usenull=f and useother=f options are used to exclude null values and other values from the chart2.
The chart command creates a table with headers that match the order of the fields and functions in the command1. The headers for the count function are prefixed with count:, and the headers for the sum function are prefixed with sum:1. The values of the product and action fields are used as the suffixes for the headers1.
Therefore, the table headers created by this command are Product, count: addtocart, count: remove, count: purchase, sum: addtocart, sum: remove, and sum: purchase1.
NEW QUESTION # 165
Based on the macro definition shown below, what is the correct way to execute the macro in a search string?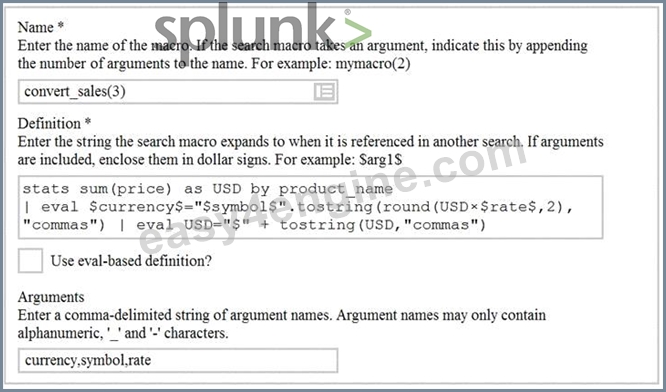
- A. Convert_sales ($euro,$€$,s79$
- B. Convert_sales (euro, €, .79)
- C. Convert_sales (euro, €, 79)"
- D. Convert_sales ($euro, $€$,S,79$)
Answer: B
Explanation:
Reference:https://docs.splunk.com/Documentation/Splunk/8.0.3/Knowledge/Usesearchmacros
The correct way to execute the macro in a search string is to use the format macro_name($arg1$, $arg2$,
...) where $arg1$, $arg2$, etc. are the arguments for the macro. In this case, the macro name
is convert_sales and it takes three arguments: currency, symbol, and rate. The arguments are enclosed in dollar
signs and separated by commas. Therefore, the correct way to execute the macro is convert_sales($euro$, $€$,
.79).
NEW QUESTION # 166
......
Free SPLK-1002 braindumps download: https://www.easy4engine.com/SPLK-1002-test-engine.html
SPLK-1002 Dumps 2024 - NewSplunk Exam Questions: https://drive.google.com/open?id=1tQOwiwkU5HVqrkpJSaXAbkm9Lt_5HCOg
