

[Nov 09, 2023] Get Up-To-Date Real Exam Questions for GCFA with New Materials
Updated GCFA Certification Exam Sample Questions
The GCFA certification exam is recognized as a valuable credential in the field of digital forensics. It is widely respected by employers and is often required for professionals who work in this field. GIAC Certified Forensics Analyst certification demonstrates that the holder has the knowledge and skills necessary to perform digital forensics investigations and to analyze and interpret data from digital devices.
NEW QUESTION # 50
HOTSPOT
Identify the port in the image given below, which can be connected to the hub to extend the number of ports, and up to 127 devices can be connected to it?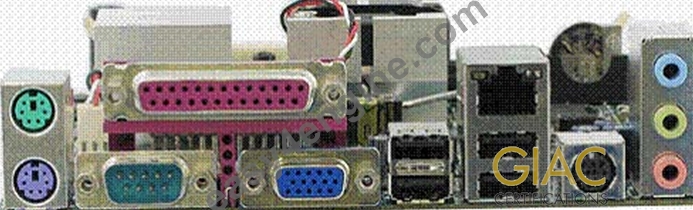
Answer:
Explanation: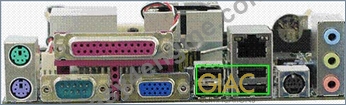
NEW QUESTION # 51
You work as a Network Administrator for Net World International. Rick, a Sales Manager, complains that his Windows 98 computer is not displaying the taskbar. You reboot his computer and find that the taskbar is still missing. How will you resolve the issue?
- A. Use Registry Editor to delete the following registry key: HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionExplorerStuckRects
- B. Replace WIN.INI from backup.
- C. Reinstall Windows 98 on Rick's computer.
- D. Copy the registry from backup.
Answer: A
NEW QUESTION # 52
Which of the following tables is formed by NTFS file system to keep the track of files, to store metadata, and their location?
- A. The Master File Table
- B. The File Allocation Table
- C. The Master Allocation Table
- D. The System File Table
Answer: A
NEW QUESTION # 53
Which of the following is included in a memory dump file?
- A. The kernel-mode call stack for the thread that stopped the process from execution
- B. Stop message and its parameters
- C. List of loaded drivers
- D. Security ID
Answer: A,B,C
Explanation:
Section: Volume C
NEW QUESTION # 54
This type of virus infects programs that can execute and load into memory to perform predefined steps for infecting systems. It infects files with the extensions .EXE, .COM, .BIN, and .SYS. As it can replicate or destroy these types of files, the operating system becomes corrupted and needs reinstallation. This type of virus is known as __________.
- A. Polymorphic virus
- B. File virus
- C. Boot sector virus
- D. Multipartite virus
- E. Stealth virus
Answer: B
NEW QUESTION # 55
You work as a Web developer for ABC Inc. You want to investigate the Cross-Site Scripting attack on your company's Web site. Which of the following methods of investigation can you use to accomplish the task?
Each correct answer represents a complete solution. Choose all that apply.
- A. Use a Web proxy to view the Web server transactions in real time and investigate any communication with outside servers.
- B. Review the source of any HTML-formatted e-mail messages for embedded scripts or links in the URL to the company's site.
- C. Look at the Web server's logs and normal traffic logging.
- D. Use Wireshark to capture traffic going to the server and then searching for the requests going to the input page, which may give log of the malicious traffic and the IP address of the source.
Answer: A,B,C
NEW QUESTION # 56
Which of the following file attributes are not available on a FAT32 partition?
Each correct answer represents a complete solution. Choose two.
- A. Hidden
- B. Compression
- C. Encryption
- D. Archive
- E. Read Only
Answer: B,C
NEW QUESTION # 57
John works as a contract Ethical Hacker. He has recently got a project to do security checking for www.we-are-secure.com. He wants to find out the operating system of the we-are-secure server in the information gathering step. Which of the following commands will he use to accomplish the task?
Each correct answer represents a complete solution. Choose two.
- A. nc 208.100.2.25 23
- B. nmap -v -O 208.100.2.25
- C. nc -v -n 208.100.2.25 80
- D. nmap -v -O www.we-are-secure.com
Answer: B,D
NEW QUESTION # 58
Based on the case study, to implement more security, which of the following additional technologies should you implement for laptop computers?
(Click the Exhibit button on the toolbar to see the case study.)
Each correct answer represents a complete solution. Choose two.
- A. Digital certificates
- B. Two-factor authentication
- C. Encrypted Data Transmissions
- D. PAP authentication
- E. Encrypting File System (EFS)
Answer: A,E
NEW QUESTION # 59
Every network device contains a unique built in Media Access Control (MAC) address, which is used to identify the authentic device to limit the network access. Which of the following addresses is a valid MAC address?
- A. F936.28A1.5BCD.DEFA
- B. A3-07-B9-E3-BC-F9
- C. 1011-0011-1010-1110-1100-0001
- D. 132.298.1.23
Answer: B
NEW QUESTION # 60
Which of the following statements are NOT true about volume boot record or Master Boot Record?
Each correct answer represents a complete solution. Choose all that apply.
- A. Four 16 bytes master partition records are present in MBR.
- B. The end of MBR marker is h55CC.
- C. The actual program can be 512 bytes long.
- D. Volume boot sector is present at cylinder 0, head 0, and sector 1 of the default boot drive.
Answer: B,C
NEW QUESTION # 61
Which of the following statements is NOT true about the file slack spaces in Windows operating system?
- A. It is possible to find user names, passwords, and other important information in slack.
- B. File slack may contain data from the memory of the system.
- C. Large cluster size will decrease the volume of the file slack.
- D. File slack is the space, which exists between the end of the file and the end of the last cluster.
Answer: C
NEW QUESTION # 62
Which of the following Windows Registry key contains the password file of the user?
- A. HKEY_LOCAL_MACHINE
- B. HKEY_USER
- C. HKEY_CURRENT_CONFIG
- D. HKEY_DYN_DATA
Answer: A
Explanation:
Section: Volume B
NEW QUESTION # 63
John works as a professional Ethical Hacker. He has been assigned the project of testing the security of www.we-are-secure.com. He has successfully completed the following pre-attack phases while testing the security of the server:
Footprinting
Scanning
Now he wants to conduct the enumeration phase. Which of the following tools can John use to conduct it?
Each correct answer represents a complete solution. Choose all that apply.
- A. PsFile
- B. WinSSLMiM
- C. UserInfo
- D. PsPasswd
Answer: A,C,D
NEW QUESTION # 64
Which of the following uses hard disk drive space to provide extra memory for a computer?
- A. File system
- B. Cluster
- C. Virtual memory
- D. RAM
Answer: C
NEW QUESTION # 65
Which of the following file systems supports the hot fixing feature?
- A. exFAT
- B. FAT32
- C. NTFS
- D. FAT16
Answer: C
NEW QUESTION # 66
Adam works as a professional Computer Hacking Forensic Investigator. A project has been assigned to him to investigate a multimedia enabled mobile phone, which is suspected to be used in a cyber crime. Adam uses a tool, with the help of which he can recover deleted text messages, photos, and call logs of the mobile phone. Which of the following tools is Adam using?
- A. FAU
- B. Galleta
- C. FTK Imager
- D. Device Seizure
Answer: D
NEW QUESTION # 67
John works as a professional Ethical Hacker. He has been assigned a project for testing the security of www.we-are-secure.com. He wants to corrupt an IDS signature database so that performing attacks on the server is made easy and he can observe the flaws in the We-are-secure server. To perform his task, he first of all sends a virus that continuously changes its signature to avoid detection from IDS. Since the new signature of the virus does not match the old signature, which is entered in the IDS signature database, IDS becomes unable to point out the malicious virus. Which of the following IDS evasion attacks is John performing?
- A. Polymorphic shell code attack
- B. Evasion attack
- C. Insertion attack
- D. Session splicing attack
Answer: A
NEW QUESTION # 68
You work as a Network Administrator for Web World Inc. You want to host an e-commerce Web site on your network. You want to ensure that storage of credit card information is secure. Which of the following conditions should be met to accomplish this?
Each correct answer represents a complete solution. Choose all that apply.
- A. Strong encryption software should be used to store credit card information.
- B. The NTFS file system should be implemented on a client computer.
- C. Only authorized access should be allowed to credit card information.
- D. NT authentication should be required for all customers before they provide their credit card numbers.
Answer: A,C
NEW QUESTION # 69
Which of the following firewalls depends on the three-way handshake of the TCP protocol?
- A. Proxy-based firewall
- B. Endian firewall
- C. Stateful firewall
- D. Packet filter firewall
Answer: C
NEW QUESTION # 70
You are working with a team that will be bringing in new computers to a sales department at a company. The sales team would like to keep not only their old files, but system settings as well on the new PC's. What should you do?
- A. Use the Disk Management tool to move everything to the new computer.
- B. Do a system backup (complete) on each old machine, then restore it onto the new machines
- C. Copy the files and the Windows Registry to a removable media then copy it onto the new machines.
- D. Use the User State Migration tool to move the system settings and files to the new machines.
Answer: D
NEW QUESTION # 71
Which of the following registry hives stores configuration information specific to a particular user who is currently logged on to the computer?
- A. HKEY_LOCAL_MACHINE
- B. HKEY_USERS
- C. HKEY_CLASSES_ROOT
- D. HKEY_CURRENT_USER
Answer: D
NEW QUESTION # 72
......
GIAC GCFA (GIAC Certified Forensics Analyst) Exam is a certification exam that tests the knowledge and skillset required to perform digital forensics investigations. GCFA exam is designed for professionals who have experience in digital forensics, incident response, and security operations. GIAC Certified Forensics Analyst certification is globally recognized and demonstrates a high level of proficiency in digital forensics analysis.
GCFA Study Guide Cover to Cover as Literally: https://www.easy4engine.com/GCFA-test-engine.html
Get Unlimited Access to GCFA Certification Exam Cert Guide: https://drive.google.com/open?id=1j3LUiae7uGv99q8_0QVBuC21N0_UZda4
