

2026 Correct and Up-to-date Google Professional-Cloud-Network-Engineer BrainDumps
Current Professional-Cloud-Network-Engineer dumps Preparation through Our Practice Test
Google Professional-Cloud-Network-Engineer certification exam is an important credential for network engineers who work with Google Cloud. It validates the skills and knowledge of professionals who can design, implement, and manage complex networks on Google Cloud that meet business requirements and performance goals. By passing Professional-Cloud-Network-Engineer exam, professionals demonstrate their expertise in Google Cloud networking services and their ability to optimize network infrastructure for maximum performance and security.
Google Professional-Cloud-Network-Engineer certification is a professional certification designed for individuals who aspire to become professional cloud network engineers. Google Cloud Certified - Professional Cloud Network Engineer certification is offered by Google Cloud and is designed to test the candidate's knowledge and skills in cloud networking technologies, best practices, and design principles. Google Cloud Certified - Professional Cloud Network Engineer certification is globally recognized and demonstrates the candidate's ability to design, implement, and manage secure, scalable, and highly available network solutions on the Google Cloud Platform.
Google Professional-Cloud-Network-Engineer certification exam is designed to evaluate the knowledge and skills of network engineers who work with Google Cloud Platform. Google Cloud Certified - Professional Cloud Network Engineer certification is ideal for professionals who are responsible for designing, implementing, and managing networks on the Google Cloud Platform. Professional-Cloud-Network-Engineer exam measures various aspects of network engineering, including designing and implementing network infrastructure, configuring network services, and optimizing network performance.
NEW QUESTION # 60
You work for a multinational enterprise that is moving to GCP.
These are the cloud requirements:
* An on-premises data center located in the United States in Oregon and New York with Dedicated Interconnects connected to Cloud regions us-west1 (primary HQ) and us-east4 (backup)
* Multiple regional offices in Europe and APAC
* Regional data processing is required in europe-west1 and australia-southeast1
* Centralized Network Administration Team
Your security and compliance team requires a virtual inline security appliance to perform L7 inspection for URL filtering. You want to deploy the appliance in us-west1.
What should you do?
- A. * Create 2 VPCs in a Shared VPC Host Project.* Configure a 2-NIC instance in zone us-west1-a in the Host Project.* Attach NIC0 in VPC #1 us-west1 subnet of the Host Project.* Attach NIC1 in VPC #2 us-west1 subnet of the Host Project.* Deploy the instance.* Configure the necessary routes and firewall rules to pass traffic through the instance.
- B. * Create 2 VPCs in a Shared VPC Host Project.* Configure a 2-NIC instance in zone us-west1-a in the Service Project.* Attach NIC0 in VPC #1 us-west1 subnet of the Host Project.* Attach NIC1 in VPC #2 us-west1 subnet of the Host Project.* Deploy the instance.* Configure the necessary routes and firewall rules to pass traffic through the instance.
- C. * Create 1 VPC in a Shared VPC Service Project.* Configure a 2-NIC instance in zone us-west1-a in the Service Project.* Attach NIC0 in us-west1 subnet of the Service Project.* Attach NIC1 in us-west1 subnet of the Service Project* Deploy the instance.* Configure the necessary routes and firewall rules to pass traffic through the instance.
- D. * Create 1 VPC in a Shared VPC Host Project.* Configure a 2-NIC instance in zone us-west1-a in the Host Project.* Attach NIC0 in us-west1 subnet of the Host Project.* Attach NIC1 in us-west1 subnet of the Host Project* Deploy the instance.* Configure the necessary routes and firewall rules to pass traffic through the instance.
Answer: A
NEW QUESTION # 61
You are deploying an application that runs on Compute Engine instances. You need to determine how to expose your application to a new customer You must ensure that your application meets the following requirements
* Maps multiple existing reserved external IP addresses to the Instance
* Processes IP Encapsulating Security Payload (ESP) traffic
What should you do?
- A. Configure a target instance, and create a protocol forwarding rule for each external IP address to be mapped to the instance.
- B. Configure a target pool, and create protocol forwarding rules for each external IP address.
- C. Configure a backend service, and create an external network load balancer for each external IP address
- D. Configure the Compute Engine Instances' network Interface external IP address from None to Ephemeral Add as many external IP addresses as required
Answer: A
Explanation:
The correct answer is C. Configure a target instance, and create a protocol forwarding rule for each external IP address to be mapped to the instance.
This answer is based on the following facts:
A target instance is a Compute Engine instance that handles traffic from one or more forwarding rules1. You can use target instances to forward traffic to a single VM instance from one or more external IP addresses2.
A protocol forwarding rule specifies the IP protocol and port range for the traffic that you want to forward3. You can use protocol forwarding rules to forward traffic of any IP protocol, including ESP4.
The other options are not correct because:
Option A is not possible. You cannot create protocol forwarding rules for a target pool. A target pool is a group of instances that receives traffic from a network load balancer5.
Option B is not suitable. You do not need to create an external network load balancer for each external IP address. An external network load balancer distributes traffic among multiple backend instances based on the destination IP address and port. You can use a single load balancer with multiple forwarding rules to map multiple external IP addresses to the same backend service.
Option D is not feasible. You cannot add multiple external IP addresses to a single network interface of a Compute Engine instance. Each network interface can have only one external IP address that is either ephemeral or static. You can use alias IP ranges to assign multiple internal IP addresses to a single network interface, but not external IP addresses.
NEW QUESTION # 62
You configured a single IPSec Cloud VPN tunnel for your organization to a third-party customer. You confirmed that the VPN tunnel is established; however, the BGP session status states that BGP is not configured. The customer has provided you with their BGP settings:
* Local BGP address: 169.254.11.1/30
* Local ASN: 64515
* Peer BGP address: 169.254.11.2
* Peer ASN: 64517
* Base MED: 1000
* MD5 Authentication: Disabled
You need to configure the local BGP session for this tunnel based on the settings provided by the customer.
You already associated the Cloud Router with the Cloud VPN Tunnel. What settings should you use for the BGP session?
- A. Peer ASN: 64515
Advertised Route Priority (MED): 100
Local BGP IP: 169.254.11.2
Peer BGP IP: 169.254.11.1
MD5 Authentication: Disabled - B. Peer ASN: 64515
Advertised Route Priority (MED): 100
Local BGP IP: 169.254.11.1
Peer BGP IP: 169.254.11.2
MD5 Authentication: Disabled - C. Peer ASN: 64517
Advertised Route Priority (MED): 100
Local BGP IP: 169.254.11.2
Peer BGP IP: 169.254.11.1
MD5 Authentication: Disabled - D. Peer ASN: 64515
Advertised Route Priority (MED): 1000
Local BGP IP: 169.254.11.2
Peer BGP IP: 169.254.11.1
MD5 Authentication: Enabled
Answer: C
Explanation:
Explanation: The correct configuration requires setting the Peer ASN as 64517 (as this is the ASN of the third-party customer). The local and peer BGP IP addresses should also be set correctly based on the provided information, and MD5 authentication should be disabled. The route priority should be set to 100 to reflect standard behavior.
NEW QUESTION # 63
You are the network administrator responsible for hybrid connectivity at your organization. Your developer team wants to use Cloud SQL in the us-west1 region in your Shared VPC. You configured a Dedicated Interconnect connection and a Cloud Router in us-west1, and the connectivity between your Shared VPC and on-premises data center is working as expected. You just created the private services access connection required for Cloud SQL using the reserved IP address range and default settings. However, your developers cannot access the Cloud SQL instance from on-premises. You want to resolve the issue. What should you do?
- A. Modify the VPC Network Peering connection used for Cloud SQL, and enable the import and export of routes.
Create a custom route advertisement in your Cloud Router to advertise the Cloud SQL IP address range. - B. Create an additional Cloud Router in us-west2.
Create a new Border Gateway Protocol (BGP) peering connection to your on-premises data center.
Modify the VPC Network Peering connection used for Cloud SQL, and enable the import and export of routes. - C. Change the VPC routing mode to global.
Create a custom route advertisement in your Cloud Router to advertise the Cloud SQL IP address range. - D. Change the VPC routing mode to global.
Modify the VPC Network Peering connection used for Cloud SQL, and enable the import and export of routes.
Answer: A
NEW QUESTION # 64
You created a new VPC network named Dev with a single subnet. You added a firewall rule for the network Dev to allow HTTP traffic only and enabled logging. When you try to log in to an instance in the subnet via Remote Desktop Protocol, the login fails. You look for the Firewall rules logs in Stackdriver Logging, but you do not see any entries for blocked traffic. You want to see the logs for blocked traffic.
What should you do?
- A. Try connecting to the instance via SSH, and check the logs.
- B. Create a new firewall rule with priority 65500 to deny all traffic, and enable logs.
- C. Check the VPC flow logs for the instance.
- D. Create a new firewall rule to allow traffic from port 22, and enable logs.
Answer: C
NEW QUESTION # 65
Your company is planning a migration to Google Kubernetes Engine. Your application team informed you that they require a minimum of 60 Pods per node and a maximum of 100 Pods per node Which Pod per node CIDR range should you use?
- A. /24
- B. /28
- C. /26
- D. /25
Answer: D
Explanation:
The correct answer is B. /25.
This answer is based on the following facts:
The Pod per node CIDR range determines the size of the IP address range that is assigned to each node for Pods1. The Pods that run on a node are allocated IP addresses from the node's assigned CIDR range1.
The size of the CIDR range corresponds to the maximum number of Pods per node. For example, a /24 CIDR range allows up to 256 IP addresses, but the default maximum number of Pods per node for Standard clusters is 1102. A /25 CIDR range allows up to 128 IP addresses, which is enough for 100 Pods per node.
The other options are not correct because:
Option A is too large. A /24 CIDR range allows more IP addresses than needed for 100 Pods per node. This could result in inefficient use of the IP address space and limit the number of nodes that can be created in the cluster.
Option C is too small. A /26 CIDR range allows only 64 IP addresses, which is not enough for 60 Pods per node. This could result in insufficient capacity to schedule Pods on the nodes.
Option D is also too small. A /28 CIDR range allows only 16 IP addresses, which is far below the minimum requirement of 60 Pods per node. This could result in Pod scheduling failures and poor performance.
NEW QUESTION # 66
All the instances in your project are configured with the custom metadata enable-oslogin value set to FALSE and to block project-wide SSH keys. None of the instances are set with any SSH key, and no project-wide SSH keys have been configured. Firewall rules are set up to allow SSH sessions from any IP address range. You want to SSH into one instance.
What should you do?
- A. Set the custom metadata enable-oslogin to TRUE, and SSH into the instance using a third-party tool like putty or ssh.
- B. Generate a new SSH key pair. Verify the format of the private key and add it to the instance.
SSH into the instance using a third-party tool like putty or ssh. - C. Generate a new SSH key pair. Verify the format of the public key and add it to the project.
SSH into the instance using a third-party tool like putty or ssh. - D. Open the Cloud Shell SSH into the instance using gcloud compute ssh.
Answer: A
Explanation:
https://cloud.google.com/compute/docs/storing-retrieving-metadata
NEW QUESTION # 67
Question:
You need to enable Private Google Access for some subnets within your Virtual Private Cloud (VPC). Your security team set up the VPC to send all internet-bound traffic back to the on-premises data center for inspection before egressing to the internet, and is also implementing VPC Service Controls for API-level security control. You have already enabled the subnets for Private Google Access. What configuration changes should you make to enable Private Google Access while adhering to your security team's requirements?
- A. Create a private DNS zone with a CNAME record for *.googleapis.com to private.googleapis.com, with an A record pointing to Google's private API address range.
Change the custom route that points the default route (0/0) to the default internet gateway as the next hop. - B. Create a private DNS zone with a CNAME record for *.googleapis.com to restricted.googleapis.com, with an A record pointing to Google's restricted API address range.Change the custom route that points the default route (0/0) to the default internet gateway as the next hop.
- C. Create a private DNS zone with a CNAME record for *.googleapis.com to private.googleapis.com, with an A record pointing to Google's private API address range.
Create a custom route that points Google's private API address range to the default internet gateway as the next hop. - D. Create a private DNS zone with a CNAME record for *.googleapis.com to restricted.googleapis.com, with an A record pointing to Google's restricted API address range.
Create a custom route that points Google's restricted API address range to the default internet gateway as the next hop.
Answer: B
Explanation:
For environments requiring API security controls, use restricted.googleapis.com as it restricts access to Google APIs and enforces VPC Service Controls. The custom DNS and routing configuration ensures compliance with security policies by directing all API traffic to restricted endpoints while maintaining Private Google Access.
Reference: Google Cloud - Private Google Access and DNS Configuration
NEW QUESTION # 68
Question:
Your organization has a subset of applications in multiple regions that require internet access. You need to control internet access from applications to URLs, including hostnames and paths. The compute instances that run these applications have an associated secure tag. What should you do?
- A. Deploy a Secure Web Proxy instance in each region. Apply a Secure Web Proxy policy to allow access from machines that match the secure tag to the URLs defined in a URL list.
- B. Deploy a single Secure Web Proxy instance with global access enabled. Apply a Secure Web Proxy policy to allow access from machines that match the secure tag to the URLs defined in a URL list.
- C. Deploy a Cloud NAT gateway. Use fully qualified domain name (FQDN) objects in the firewall policy rules to filter outgoing traffic to specific domains from machines that match a service account.
- D. Deploy a Cloud NAT gateway. Use fully qualified domain name (FQDN) objects in the firewall policy rules to filter outgoing traffic to specific domains from machines that match the secure tag.
Answer: B
Explanation:
To control internet access on a per-URL basis (including hostname and path), you should deploy Secure Web Proxy with global access enabled. The Secure Web Proxy will allow policy-based filtering of web traffic, allowing control over which URLs can be accessed based on the URL list defined in the policy. Unlike Cloud NAT, which does not support FQDN filtering, Secure Web Proxy is designed to provide such control, especially for scenarios with sensitive or controlled internet access requirements.
NEW QUESTION # 69
You are designing an IP address scheme for new private Google Kubernetes Engine (GKE) clusters, Due to IP address exhaustion of the RFC 1918 address space in your enterprise, you plan to use privately used public IP space for the new dusters. You want to follow Google-recommended practices, What should you do after designing your IP scheme?
- A. Create the minimum usable RFC 1918 primary and secondary subnet IP ranges for the clusters Re-use the secondary address range for the services across multiple private GKE clusters.
- B. Create privately used public IP primary and secondary subnet ranges for the clusters. Create a private GKE cluster With the following options selected and - siable-default-snat,--enable-ip-alias, and -enable-private-nodes
- C. Create privately used public IP primary and secondary subnet ranges for the clusters. Create a private GKE cluster With the following options selected: --enab1e-ip-a1ias and --enable-private-nodes.
- D. Create the minimum usable RFC 1918 primary and secondary subnet IP ranges for the clusters. Re-use the secondary address range for the pods across multiple private GKE clusters.
Answer: B
Explanation:
The correct answer is D. Create privately used public IP primary and secondary subnet ranges for the clusters. Create a private GKE cluster with the following options selected: --disable-default-snat, --enable-ip-alias, and --enable-private-nodes.
This answer is based on the following facts:
Privately used public IP (PUPI) addresses are any public IP addresses not owned by Google that a customer can use privately on Google Cloud1. You can use PUPI addresses for GKE pods and services in private clusters to mitigate address exhaustion.
A private GKE cluster is a cluster that has no public IP addresses on the nodes2. You can use private clusters to isolate your workloads from the public internet and enhance security.
The --disable-default-snat option disables source network address translation (SNAT) for the cluster3. This option allows you to use PUPI addresses without conflicting with other public IP addresses on the internet.
The --enable-ip-alias option enables alias IP ranges for the cluster4. This option allows you to use separate subnet ranges for nodes, pods, and services, and to specify the size of those ranges.
The --enable-private-nodes option enables private nodes for the cluster5. This option ensures that the nodes have no public IP addresses and can only communicate with other Google Cloud resources in the same VPC network or peered networks.
The other options are not correct because:
Option A is not suitable. Creating RFC 1918 primary and secondary subnet IP ranges for the clusters does not solve the problem of address exhaustion. Re-using the secondary address range for pods across multiple private GKE clusters can cause IP conflicts and routing issues.
Option B is also not suitable. Creating RFC 1918 primary and secondary subnet IP ranges for the clusters does not solve the problem of address exhaustion. Re-using the secondary address range for services across multiple private GKE clusters can cause IP conflicts and routing issues.
Option C is not feasible. Creating privately used public IP primary and secondary subnet ranges for the clusters is a valid step, but creating a private GKE cluster with only --enable-ip-alias and --enable-private-nodes options is not enough. You also need to disable default SNAT to avoid IP conflicts with other public IP addresses on the internet.
NEW QUESTION # 70
You created a VPC network named Retail in auto mode. You want to create a VPC network named Distribution and peer it with the Retail VPC.
How should you configure the Distribution VPC?
- A. Rename the default VPC as "Distribution" and peer it via network peering.
- B. Create the Distribution VPC in custom mode. Use the CIDR range 10.128.0.0/9. Create the necessary subnets, and then peer them via network peering.
- C. Create the Distribution VPC in custom mode. Use the CIDR range 10.0.0.0/9. Create the necessary subnets, and then peer them via network peering.
- D. Create the Distribution VPC in auto mode. Peer both the VPCs via network peering.
Answer: C
NEW QUESTION # 71
You work for one of the biggest digital media company in USA .The company management has decided to move 90 TB of backups and archival data to Google Cloud. They are looking for long term cost effective archival storage for disaster recovery in Google Cloud . Please select the right solution.
- A. Transfer Appliance and Nearline storage
- B. Transfer Appliance and Coldline storage
- C. gsutil and Cloud storage
- D. Storage Transfer and Nearline storage
Answer: B
Explanation:
Option B is the correct choice because ,Transfer Appliance is the best choice moving large volume of data and since they are looking for long term cost effective disaster recovery solution , coldline is the best option.
Option A is Incorrect because Storage Transfer is used to import online data into Cloud Storage .
Your online data source can be an Amazon Simple Storage Service (Amazon S3) bucket, an HTTP/HTTPS location, or a Cloud Storage bucket Option C is Incorrect because , gsutil isn't recommended for large volume of data transfer ,It will take a very long time for data transfer depending on the bandwidth.
Option D is Incorrect because , Coldline is a more cost effective archival storage for disaster recovery.
NEW QUESTION # 72
You are developing an HTTP API hosted on a Compute Engine virtual machine instance that must be invoked only by multiple clients within the same Virtual Private Cloud (VPC). You want clients to be able to get the IP address of the service. What should you do?
- A. Reserve a static external IP address and assign it to an HTTP(S) load balancing service's forwarding rule. Clients should use this IP address to connect to the service.
- B. Ensure that clients use Compute Engine internal DNS by connecting to the instance name with the url
https://[API_NAME]/[API_VERSION]/. - C. Ensure that clients use Compute Engine internal DNS by connecting to the instance name with the url
https://[INSTANCE_NAME].[ZONE].c.[PROJECT_ID].internal/. - D. Reserve a static external IP address and assign it to an HTTP(S) load balancing service's forwarding rule. Then, define an A record in Cloud DNS. Clients should use the name of the A record to connect to the service.
Answer: D
NEW QUESTION # 73
You have the following private Google Kubernetes Engine (GKE) cluster deployment: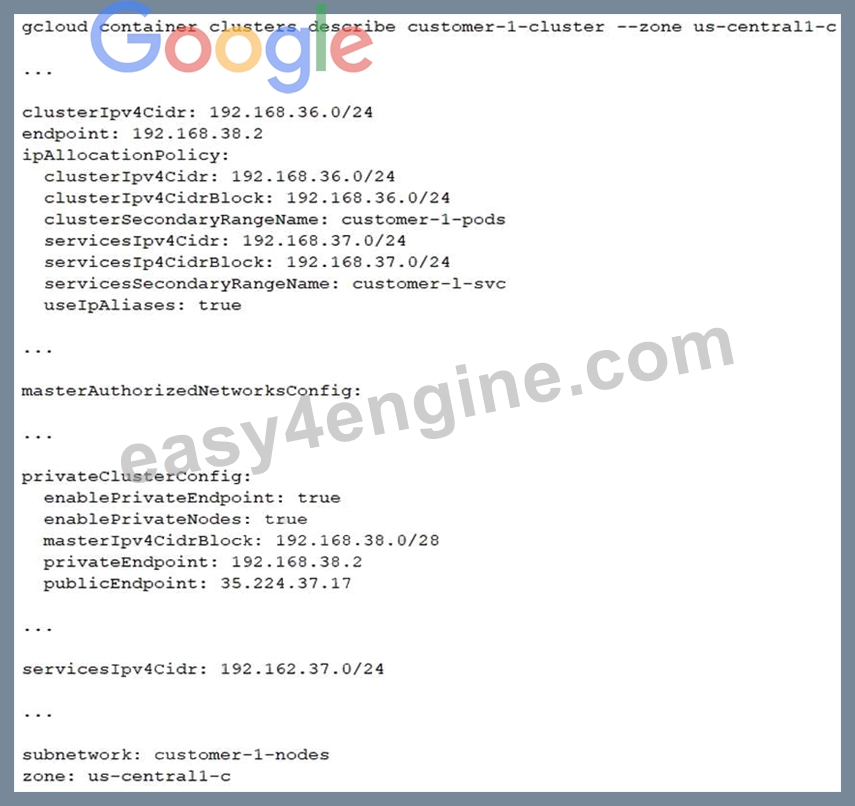
You have a virtual machine (VM) deployed in the same VPC in the subnetwork kubernetes-management with internal IP address 192.168.40 2/24 and no external IP address assigned. You need to communicate with the cluster master using kubectl. What should you do?
- A. Add the network 192.168.38.0/28 to the masterAuthorizedNetworksConfig. Configure kubectl to communicate with the endpoint 192.168.38.2
- B. Add the network 192.168.36.0/24 to the masterAuthorizedNetworksConfig. Configure kubectl to communicate with the endpoint 192.168.38.2
- C. Add the network 192.168.40.0/24 to the masterAuthorizedNetworksConfig. Configure kubectl to communicate with the endpoint 192.168.38.2.
- D. Add an external IP address to the VM, and add this IP address in the masterAuthorizedNetworksConfig. Configure kubectl to communicate with the endpoint 35.224.37.17.
Answer: C
NEW QUESTION # 74
Your organization is deploying a single project for 3 separate departments. Two of these departments require network connectivity between each other, but the third department should remain in isolation. Your design should create separate network administrative domains between these departments. You want to minimize operational overhead.
How should you design the topology?
- A. Create 3 separate VPCs, and use VPC peering to establish connectivity between the two appropriate VPCs.
- B. Create a Shared VPC Host Project and the respective Service Projects for each of the 3 separate departments.
- C. Create a single project, and deploy specific firewall rules. Use network tags to isolate access between the departments.
- D. Create 3 separate VPCs, and use Cloud VPN to establish connectivity between the two appropriate VPCs.
Answer: B
Explanation:
Use Shared VPC to connect to a common VPC network. Resources in those projects can communicate with each other securely and efficiently across project boundaries using internal IPs. You can manage shared network resources, such as subnets, routes, and firewalls, from a central host project, enabling you to apply and enforce consistent network policies across the projects.
With Shared VPC and IAM controls, you can separate network administration from project administration. This separation helps you implement the principle of least privilege. For example, a centralized network team can administer the network without having any permissions into the participating projects. Similarly, the project admins can manage their project resources without any permissions to manipulate the shared network.
Reference: https://cloud.google.com/docs/enterprise/best-practices-for-enterprise-organizations
NEW QUESTION # 75
Your company has just launched a new critical revenue-generating web application. You deployed the application for scalability using managed instance groups, autoscaling, and a network load balancer as frontend. One day, you notice severe bursty traffic that caused autoscaling to reach the maximum number of instances, and users of your application cannot complete transactions. After an investigation, you think it is a DDOS attack. You want to quickly restore user access to your application and allow successful transactions while minimizing cost.
Which two steps should you take? (Choose two.)
- A. Create a global HTTP(s) load balancer and move your application backend to this load balancer.
- B. Increase the maximum autoscaling backend to accommodate the severe bursty traffic.
- C. Shut down the entire application in GCP for a few hours. The attack will stop when the application is offline.
- D. Use Cloud Armor to blacklist the attacker's IP addresses.
- E. SSH into the backend compute engine instances, and view the auth logs and syslogs to further understand the nature of the attack.
Answer: B,E
NEW QUESTION # 76
Question:
Your organization has a hub and spoke architecture with VPC Network Peering, and hybrid connectivity is centralized at the hub. The Cloud Router in the hub VPC is advertising subnet routes, but the on-premises router does not appear to be receiving any subnet routes from the VPC spokes. You need to resolve this issue.
What should you do?
- A. Create custom routes at the Cloud Router in the hub to advertise the subnets of the VPC spokes.
- B. Create custom routes at the Cloud Router in the spokes to advertise the subnets of the VPC spokes.
- C. Create a BGP route policy at the Cloud Router, and ensure the subnets of the VPC spokes are being announced towards the on-premises environment.
- D. Create custom learned routes at the Cloud Router in the hub to advertise the subnets of the VPC spokes.
Answer: D
Explanation:
Creating custom learned routes at the hub's Cloud Router is required for advertising VPC spokes' subnets to the on-premises environment. This centralizes route configuration and ensures that all spoke subnet routes are propagated to the hybrid network.
Reference: Google Cloud - Cloud Router Custom Routes
NEW QUESTION # 77
You are using a 10-Gbps direct peering connection to Google together with the gsutil tool to upload files to Cloud Storage buckets from on-premises servers. The on-premises servers are 100 milliseconds away from the Google peering point. You notice that your uploads are not using the full 10-Gbps bandwidth available to you. You want to optimize the bandwidth utilization of the connection.
What should you do on your on-premises servers?
- A. Compress files using utilities like tar to reduce the size of data being sent.
- B. Tune TCP parameters on the on-premises servers.
- C. Remove the -m flag from the gsutil command to enable single-threaded transfers.
- D. Use the perfdiag parameter in your gsutil command to enable faster performance: gsutil perfdiag gs://
[BUCKET NAME].
Answer: B
Explanation:
https://cloud.google.com/solutions/tcp-optimization-for-network-performance-in-gcp-and-hybrid
https://cloud.google.com/solutions/tcp-optimization-for-network-performance-in-gcp-and-hybrid https://cloud.
google.com/blog/products/gcp/5-steps-to-better-gcp-network-performance?hl=ml
NEW QUESTION # 78
You configured a single IPSec Cloud VPN tunnel for your organization to a third-party customer. You confirmed that the VPN tunnel is established; however, the BGP session status states that BGP is not configured. The customer has provided you with their BGP settings:
Local BGP address: 169.254.11.1/30
Local ASN: 64515
Peer BGP address: 169.254.11.2
Peer ASN: 64517
Base MED: 1000
MD5 Authentication: Disabled
You need to configure the local BGP session for this tunnel based on the settings provided by the customer. You already associated the Cloud Router with the Cloud VPN Tunnel. What settings should you use for the BGP session?
- A. Peer ASN: 64515
Advertised Route Priority (MED): 100
Local BGP IP: 169.254.11.2
Peer BGP IP: 169.254.11.1
MD5 Authentication: Disabled - B. Peer ASN: 64515
Advertised Route Priority (MED): 100
Local BGP IP: 169.254.11.1
Peer BGP IP: 169.254.11.2
MD5 Authentication: Disabled - C. Peer ASN: 64517
Advertised Route Priority (MED): 100
Local BGP IP: 169.254.11.2
Peer BGP IP: 169.254.11.1
MD5 Authentication: Disabled - D. Peer ASN: 64515
Advertised Route Priority (MED): 1000
Local BGP IP: 169.254.11.2
Peer BGP IP: 169.254.11.1
MD5 Authentication: Enabled
Answer: C
Explanation:
The correct configuration requires setting the Peer ASN as 64517 (as this is the ASN of the third-party customer). The local and peer BGP IP addresses should also be set correctly based on the provided information, and MD5 authentication should be disabled. The route priority should be set to 100 to reflect standard behavior.
NEW QUESTION # 79
You are implementing a VPC architecture for your organization by using a Network Connectivity Center hub and spoke topology:
* There is one Network Connectivity Center hybrid spoke to receive on-premises routes.
* There is one VPC spoke that needs to be added as a Network Connectivity Center spoke.
Your organization has limited routable IP space fortheir cloud environment (192.168.0.0/20). The Network Connectivity Center spoke VPC is connected to on-premises with a Cloud Interconnect connection in the us- east4 region. The on-premises IP range is 172.16.0.0/16. You need to reach on-premises resources from multiple Google Cloud regions (us-westl, europe-centrall, and asia-southeastl) and minimize the IP addresses being used. What should you do?
- A. O 1- Configure a Private NAT gateway instance in us-westl (172.16.1.0/24), europe-centrall (172.16.2.0
/24), and asia-southeastl (172.16.3.0/24).
2. Add the VPC as a spoke and configure an export include policy on the VPC spoke to advertise only the NAT subnets 172.16.1.0/24, 172.16.2.0/24, and 172.16.3.0/24 to the hub.
3. Enable global dynamic to allow resources in us-westl, us-centrall, and asia-southeastl to reach the on- premises location through us-east4. - B. Q 1. Configure a Private NAT gateway instance in us-westl (192.168.1.0/24), europe-centrall (192.168.2.0/24), and asia-southeastl (192.168.3.0/24).
2. Add the VPC as a spoke and configure an export exclude policy on the VPC spoke to advertise only the NAT subnets 192.168.1.0/24, 192.168.2.0/24, and 192.168.3.0/24 to the hub.
3. Enable global dynamic routing to allow resources in us-westl, us-centrall, and asia-southeastl to reach the on-premises location through us-east4. - C. Q 1. Configure a Private NAT gateway instance in us-east4 (192.168.1.0/24).
2. Add the VPC as a spoke and configure an export include policy on the VPC spoke to advertise
192.168.1.0/24 to the hub.
3. Enable global dynamic routing to allow resources in us-westl, us-centrall and asia-southeast l to reach the on-premises location through us-east 4. - D. O 1. Configure a Private NAT gateway and NAT subnet in us-westl (192.168.1.0/24), europe-centrall (192.168.2.0/24) and asia-southeastl (192.168.3.0/24).
2. Add the VPC as a spoke and configure an export include policy to advertise only 192.168.1.0/24,
192.168.2.0/24, and 192.168.3.0/24 to the hub.
3. Enable global dynamic routing to allow resources in us-westl, us-centrall and asia-southeastl to reach the on-premises location through us-east4.
Answer: C
Explanation:
The key requirements are: limited IP space (192.168.0.0/20), reaching on-premises (172.16.0.0/16) from multiple Google Cloud regions (us-west1, europe-central1, asia-southeast1), and minimizing IP addresses used. The Cloud Interconnect connection to on-premises is in us-east4.
Minimize IP addresses and centralized NAT: Since all traffic to on-premises will traverse the Cloud Interconnect in us-east4, it's most efficient to configure a single Private NAT gateway instance in us-east4.
This allows resources from other regions to egress to on-premises through this single NAT gateway, using a minimal NAT subnet (192.168.1.0/24 in this case), thus conserving the limited 192.168.0.0/20 IP space.
Network Connectivity Center Spoke Export Policy: The VPC spoke needs to advertise the NAT subnet to the Network Connectivity Center hub. An export include policy is used to specify which routes (in this case, the
192.168.1.0/24 NAT subnet) should be advertised to the hub.
Global Dynamic Routing: To allow resources in us-west1, europe-central1, and asia-southeast1 to reach the on-premises location through the us-east4 Cloud Interconnect and NAT gateway, the VPC containing these resources (the spoke VPC) must have global dynamic routing enabled. This ensures that routes learned in one region (like the on-premises routes via us-east4) are available to VMs in all other regions of that VPC.
Options A and B configure Private NAT gateways in multiple regions, which consumes more IP addresses than necessary given that the Cloud Interconnect is only in us-east4. Option D uses 172.16.x.x for NAT subnets, which clashes with the on-premises IP range and the requirement to use the 192.168.0.0/20 space for cloud.
Exact Extract:
"Private NAT allows instances with private IP addresses in one VPC network to connect to on-premises or other cloud networks through a NAT IP address in a different region or network."
"To allow VMs in multiple regions to reach a central destination through a NAT gateway located in a specific region, you must configure global dynamic routing on the VPC network. This ensures that routes to the NAT gateway's subnet are propagated across all regions."
"When using Network Connectivity Center spokes, you can use export policies to control which routes are advertised from a spoke to the hub. An include policy specifies the exact prefixes to advertise."Reference:
Google Cloud Private NAT Documentation, Network Connectivity Center Documentation - Spoke policies, VPC Network Documentation - Dynamic routing mode
NEW QUESTION # 80
You are planning to use Terraform to deploy the Google Cloud infrastructure for your company The design must meet the following requirements
* Each Google Cloud project must represent an Internal project that your team Will work on
* After an internal project is finished, the infrastructure must be deleted
* Each Internal project must have Its own Google Cloud project owner to manage the Google Cloud resources-
* You have 10-100 projects deployed at a time,
While you are writing the Terraform code, you need to ensure that the deployment IS Simple, and the code IS reusable With centralized management What should you doo
- A. Create a Shared VPC and service project for each Internal project
- B. Create a Single pt0Ject and additional VPCs for each Internal project
- C. Create a Single Project and Single VPC for each internal project
- D. Create a single Shared VPC and attach each Google Cloud project as a service project
Answer: D
Explanation:
The correct answer is C. Create a single Shared VPC and attach each Google Cloud project as a service project.
This answer is based on the following facts:
A Shared VPC allows you to share one or more VPC networks across multiple Google Cloud projects1. This simplifies the deployment and management of the network infrastructure, as you only need to create and maintain one VPC network for all your internal projects.
A Shared VPC consists of a host project that owns the VPC network and one or more service projects that use the VPC network2. You can attach and detach service projects as needed, depending on the lifecycle of your internal projects. You can also delete service projects without affecting the host project or other service projects.
A Shared VPC allows you to delegate administrative roles to different project owners3. You can grant the Shared VPC Admin role to the owner of the host project, who can manage the VPC network and its subnets. You can also grant the Service Project Admin role to the owners of the service projects, who can manage the Google Cloud resources in their own projects.
The other options are not correct because:
Option A is not suitable. Creating a single project and additional VPCs for each internal project will increase the complexity and cost of the network infrastructure. You will need to create and maintain multiple VPC networks, firewall rules, routes, and VPN tunnels. You will also have a limit on the number of VPC networks per project4.
Option B is not feasible. Creating a single project and single VPC for each internal project will not meet the requirement of having separate project owners for each internal project. You will have only one project owner who can manage all the Google Cloud resources in the same project.
Option D is not optimal. Creating a Shared VPC and service project for each internal project will not meet the requirement of having a simple and reusable code with centralized management. You will need to create and maintain multiple Shared VPCs, which will increase the complexity and cost of the network infrastructure. You will also have more Terraform code to write and manage for each Shared VPC.
NEW QUESTION # 81
Question:
Your multi-region VPC has had a long-standing HA VPN configured in "region 1" connected to your corporate network. You are planning to add two 10 Gbps Dedicated Interconnect connections and VLAN attachments in "region 2" to connect to the same corporate network. You need to plan for connectivity between your VPC and corporate network to ensure that traffic uses the Dedicated Interconnect connections as the primary path and the HA VPN as the secondary path. What should you do?
- A. Enable global dynamic routing mode on the VPC. Configure BGP associated with the HA VPN in
"region 1" to use a base priority value of 20000. Configure BGP associated with the VLAN attachments to use a base priority of 100. Configure your on-premises routers to use similar multi-exit discriminator (MED) values. - B. Enable global dynamic routing mode on the VPC. Configure BGP associated with the HA VPN in
"region 1" to use a base priority value of 100. Configure BGP associated with the VLAN attachments to use a base priority of 20000. Configure your on-premises routers to use similar multi-exit discriminator (MED) values. - C. Enable regional dynamic routing mode on the VPC. Configure BGP associated with the HA VPN in
"region 1" to use a base priority value of 100. Configure BGP associated with the VLAN attachments to use a base priority of 20000. Configure your on-premises routers to use similar multi-exit discriminator (MED) values. - D. Enable regional dynamic routing mode on the VPC. Configure BGP associated with the HA VPN in
"region 1" to use a base priority value of 20000. Configure BGP associated with the VLAN attachments to use a base priority of 100. Configure your on-premises routers to use similar multi-exit discriminator (MED) values.
Answer: B
Explanation:
For the Dedicated Interconnect to be the primary connection over the HA VPN, you should:
Enable global dynamic routing mode to allow the VPC to distribute routes dynamically across regions.
Set the BGP priority for the VLAN attachments associated with the Dedicated Interconnect to a lower base priority (e.g., 100) than the HA VPN's priority (e.g., 20000) to ensure it is preferred.
Setting up global dynamic routing with adjusted BGP priorities on both Interconnect and VPN will allow dynamic routing of traffic based on set preferences and path attributes, such as MED and priority levels. This setup ensures the Dedicated Interconnect, with a lower priority value, becomes the primary path for traffic, while the HA VPN, with a higher priority, serves as a backup.
Reference: Google Cloud - Cloud Interconnect
Reference: Google Cloud - HA VPN Overview
NEW QUESTION # 82
......
100% Reliable Microsoft Professional-Cloud-Network-Engineer Exam Dumps Test Pdf Exam Material: https://www.easy4engine.com/Professional-Cloud-Network-Engineer-test-engine.html
Based on Official Syllabus Topics of Actual Google Professional-Cloud-Network-Engineer Exam: https://drive.google.com/open?id=1ZVaGj7asrwVrk0Kq2KRfeN_4ZHosxaSl
