

Microsoft AZ-900 Real 2022 Braindumps Mock Exam Dumps
AZ-900 Exam Questions | Real AZ-900 Practice Dumps
NEW QUESTION 92
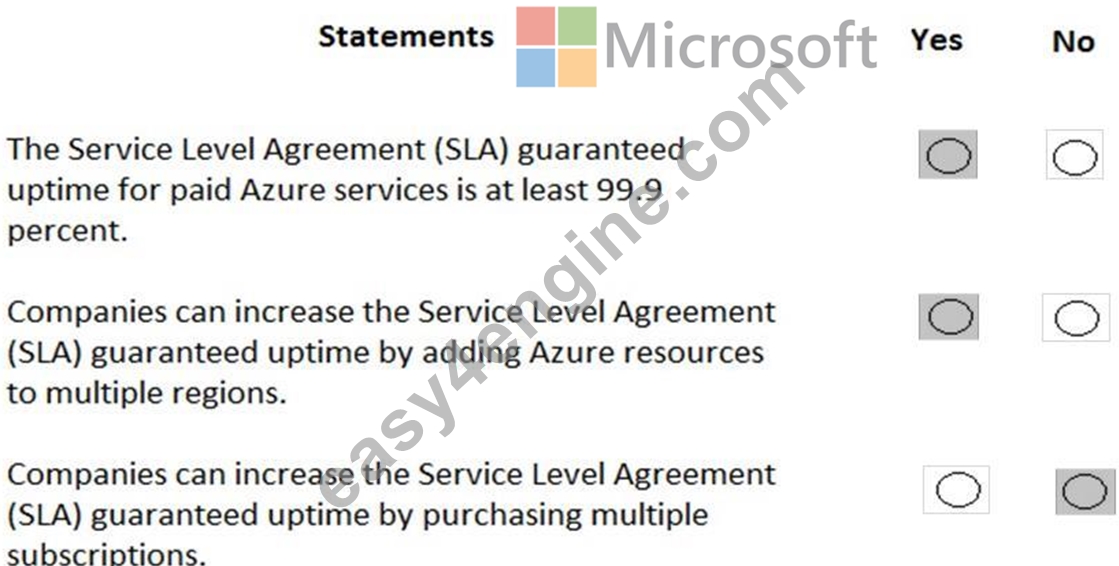
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.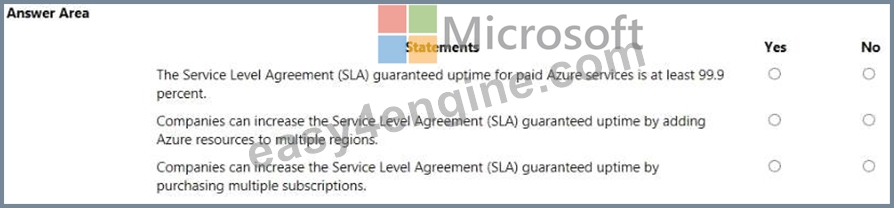
Answer:
Explanation: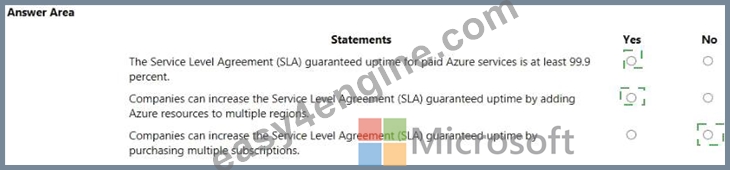
NEW QUESTION 93
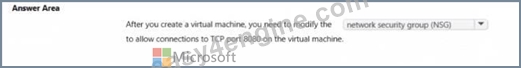
Select the answer that correctly completes the sentence.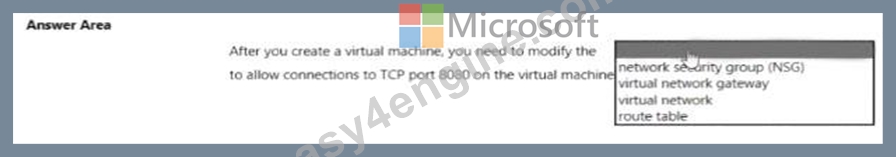
Answer:
Explanation: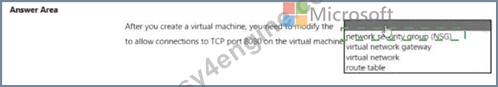
NEW QUESTION 94
Your network contains an Active Directory forest. The forest contains 5,000 user accounts.
Your company plans to migrate all network resources to Azure and to decommission the on-premises data
center.
You need to recommend a solution to minimize the impact on users after the planned migration.
What should you recommend?
- A. Create a guest user account in Azure Active Directory (Azure AD) for each user
- B. Implement Azure Multi-Factor Authentication (MFA)
- C. Sync all the Active Directory user accounts to Azure Active Directory (Azure AD)
- D. Instruct all users to change their password
Answer: C
NEW QUESTION 95
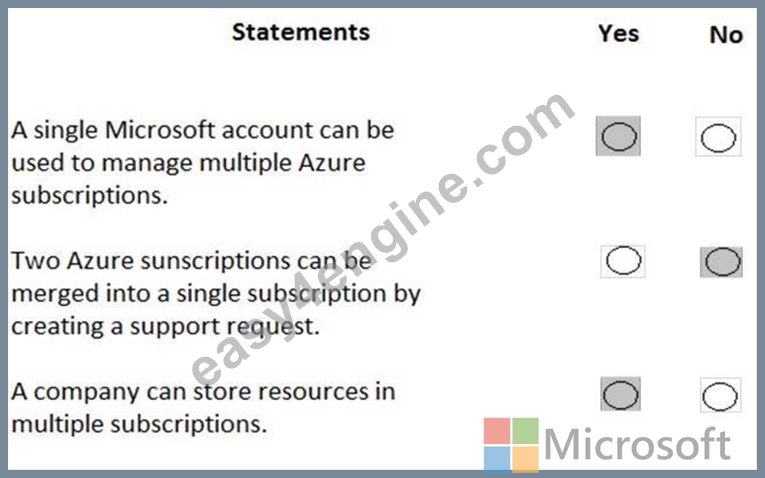
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.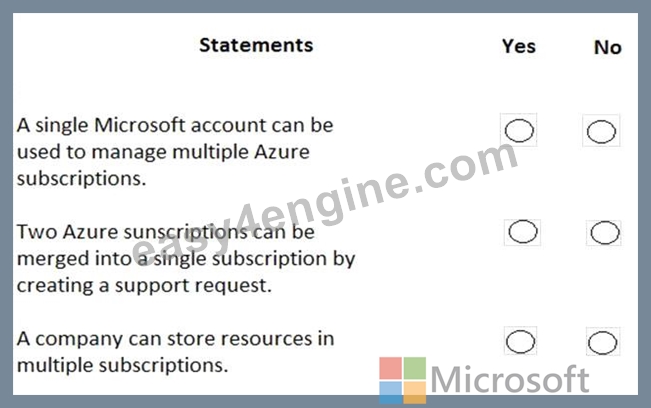
Answer:
Explanation: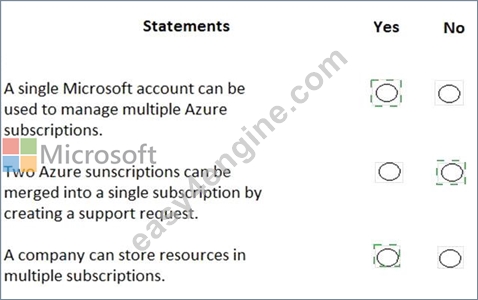
NEW QUESTION 96
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.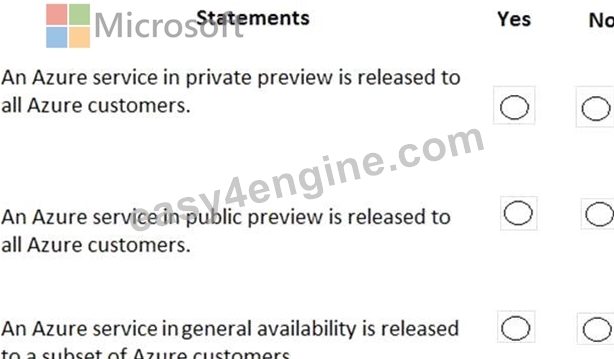
Answer:
Explanation: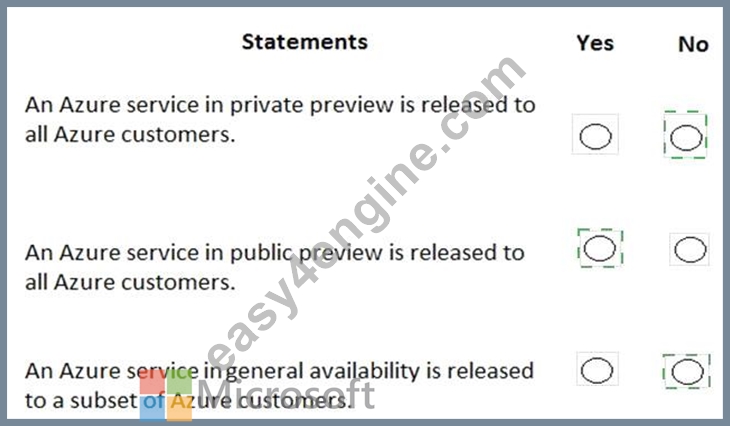
Explanation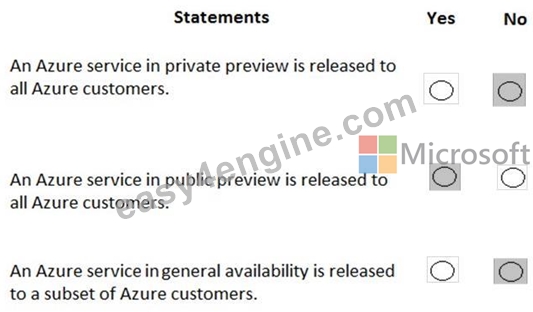
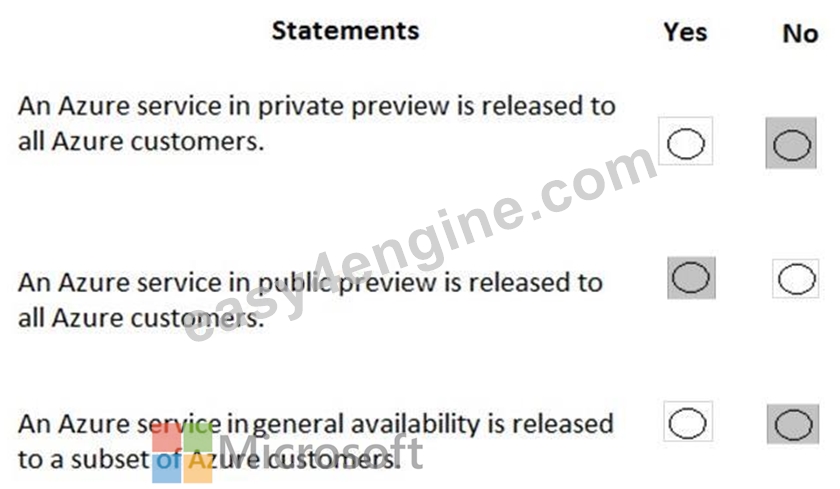
Box 1: No
Most services go to private preview then public preview before being released to general availability. The private preview is only available to certain Azure customers for evaluation purposes.
Box 2: Yes
Public Preview means that the service is in public beta and can be tried out by anyone with an Azure subscription. Services in public preview are often offered at a discount price.
Public previews are excluded from SLAs and in some cases, no support is offered.
Box 3: No
An Azure service in general availability is available to all Azure customers, not just a subset of the customers.
References:
https://azure-overview.com/Home/Faq
NEW QUESTION 97
Your network contains an Active Directory forest. The forest contains 5,000 user accounts.
Your company plans to migrate all network resources to Azure and to decommission the on-premises data center.
You need to recommend a solution to minimize the impact on users after the planned migration.
What should you recommend?
- A. Create a guest user account in Azure Active Directory (Azure AD) for each user
- B. Implement Azure Multi-Factor Authentication (MFA)
- C. Sync all the Active Directory user accounts to Azure Active Directory (Azure AD)
- D. Instruct all users to change their password
Answer: C
Explanation:
Section: Describe identity, governance, privacy, and compliance features Explanation:
To migrate to Azure and decommission the on-premises data center, you would need to create the 5,000 user accounts in Azure Active Directory. The easy way to do this is to sync all the Active Directory user accounts to Azure Active Directory (Azure AD). You can even sync their passwords to further minimize the impact on users.
The tool you would use to sync the accounts is Azure AD Connect. The Azure Active Directory Connect synchronization services (Azure AD Connect sync) is a main component of Azure AD Connect. It takes care of all the operations that are related to synchronize identity data between your on-premises environment and Azure AD.
References:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-sync-whatis
NEW QUESTION 98
To complete the sentence, select the appropriate option in the answer area.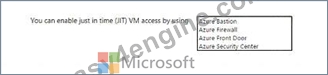
Answer:
Explanation: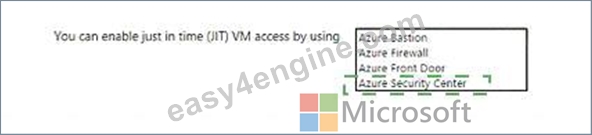
NEW QUESTION 99
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company has an Azure subscription that contains the following unused resources:
* 20 user accounts in Azure Active Directory (Azure AD)
* Five groups in Azure AD
* 10 public IP addresses
* 10 network interfaces
You need to reduce the Azure costs for the company.
Solution: You remove the unused public IP addresses.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Section: Describe Azure cost management and Service Level Agreements
Explanation:
You are charged for public IP addresses. Therefore, deleting unused public IP addresses will reduce the Azure costs.
Reference:
https://docs.microsoft.com/en-us/azure/advisor/advisor-cost-recommendations#reduce-costs-by-deleting-or- reconfiguring-idle-virtual-network-gateways
NEW QUESTION 100
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.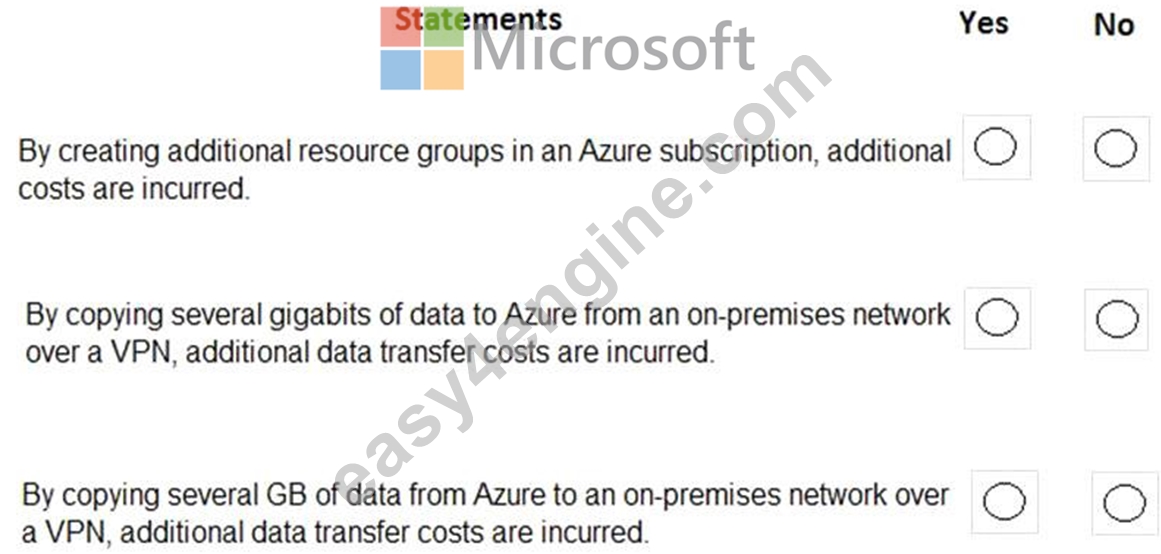
Answer:
Explanation: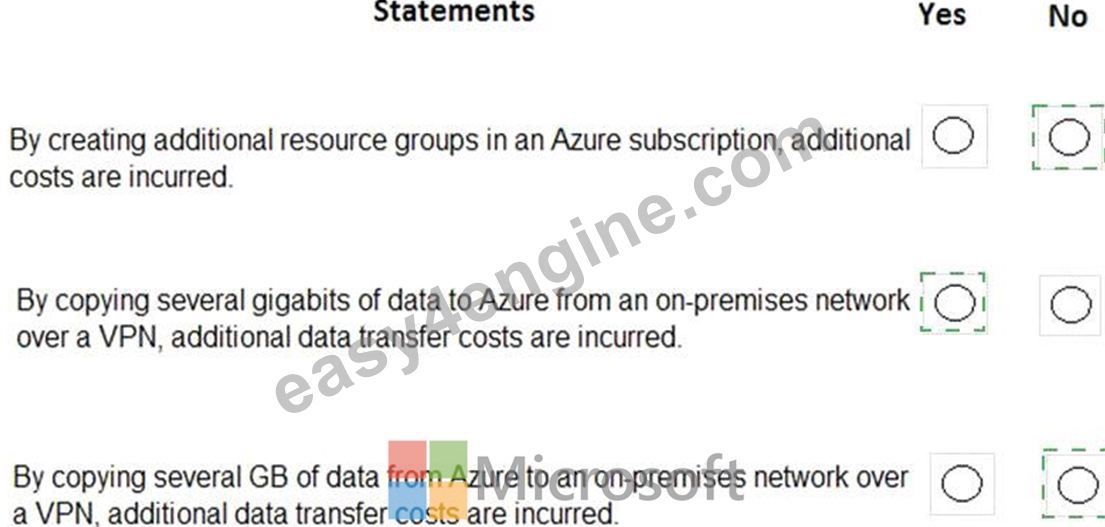
Explanation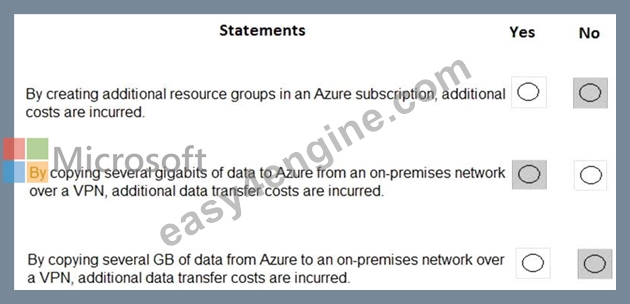
References:
https://docs.microsoft.com/en-us/azure/azure-resource-manager/manage-resource-groups-portal
https://azure.microsoft.com/en-us/pricing/details/bandwidth/
NEW QUESTION 101
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.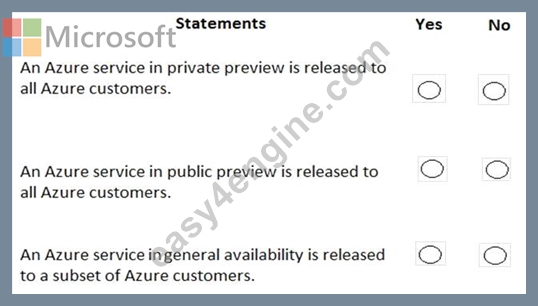
Answer:
Explanation: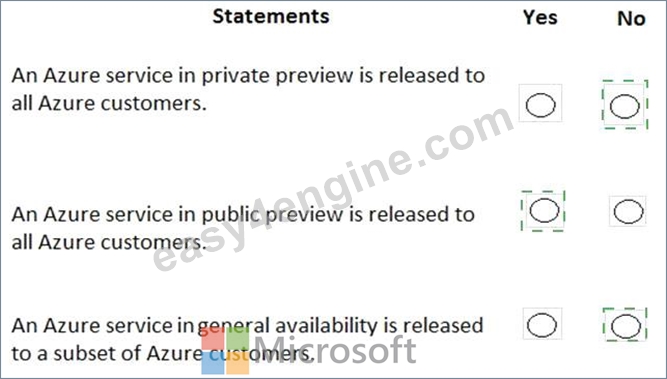
NEW QUESTION 102
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.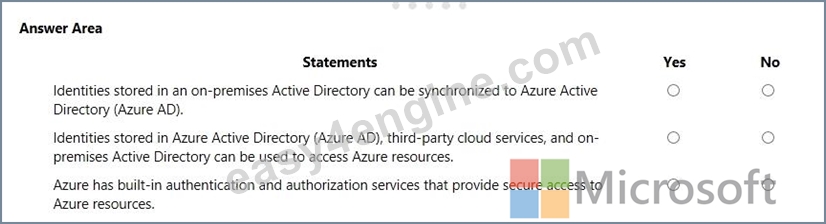
Answer:
Explanation: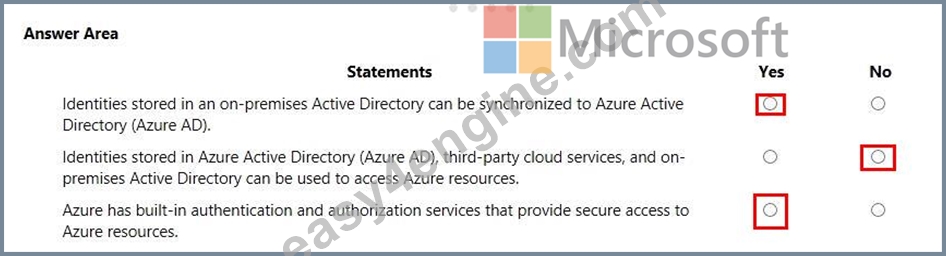
NEW QUESTION 103
Several support engineers plan to manage Azure by using the computers shown in the following table: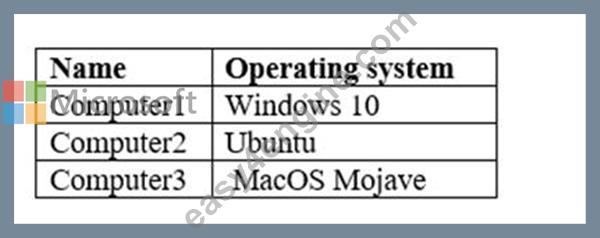
You need to identify which Azure management tools can be used from each computer.
What should you identify for each computer? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.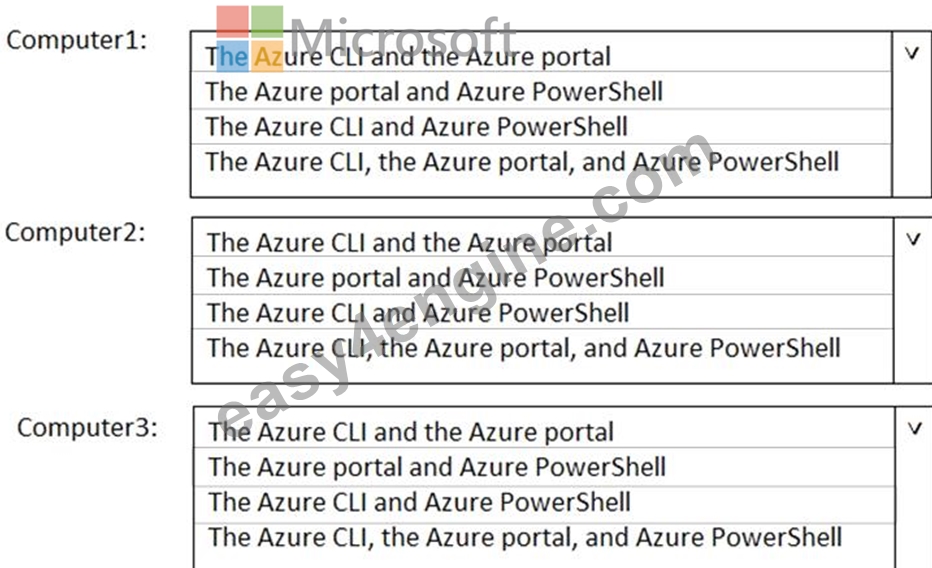
Answer:
Explanation: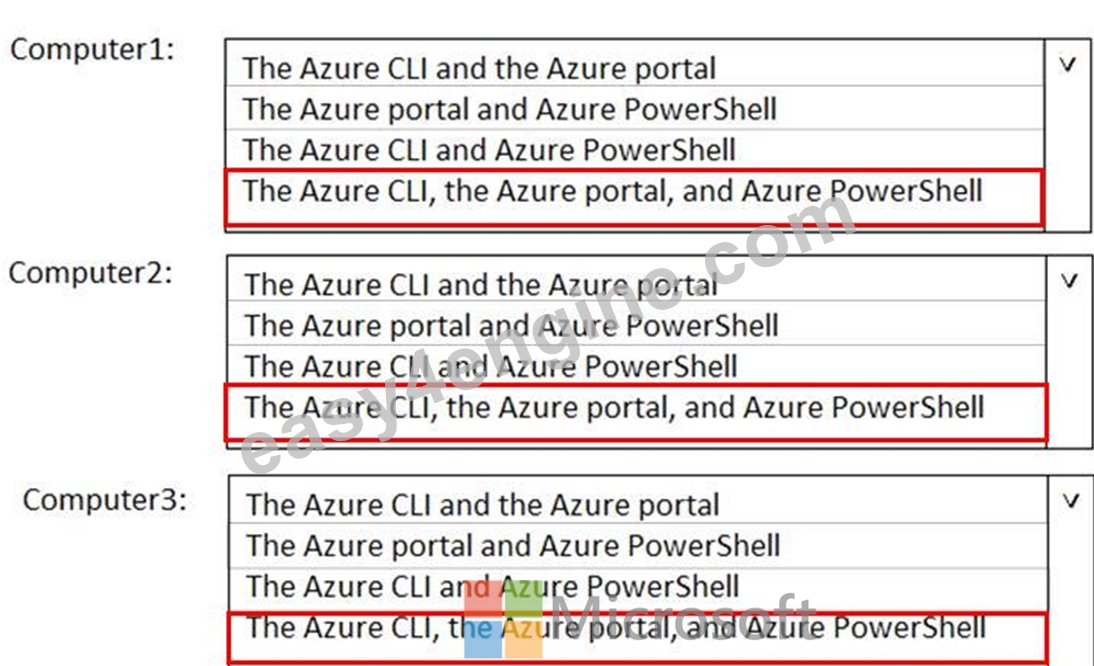
Explanation:
References:
https://buildazure.com/2016/08/18/powershell-now-open-source-and-cross-platform-linux-macos-windows/
NEW QUESTION 104
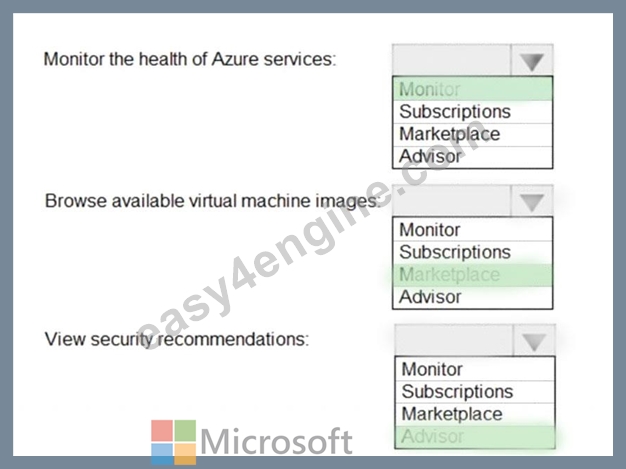
You need to identify which blades in the Azure portal must be used to perform the following tasks:
* View security recommendations.
* Monitor the health of Azure services.
* Browse available virtual machine images.
Which blade should you identify for each task? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.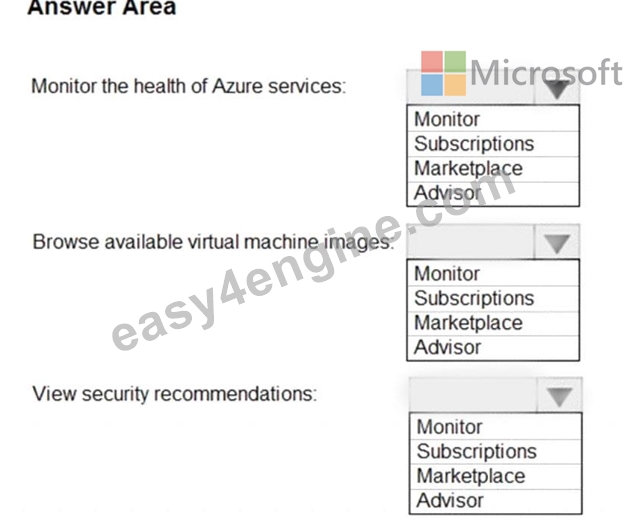
Answer:
Explanation: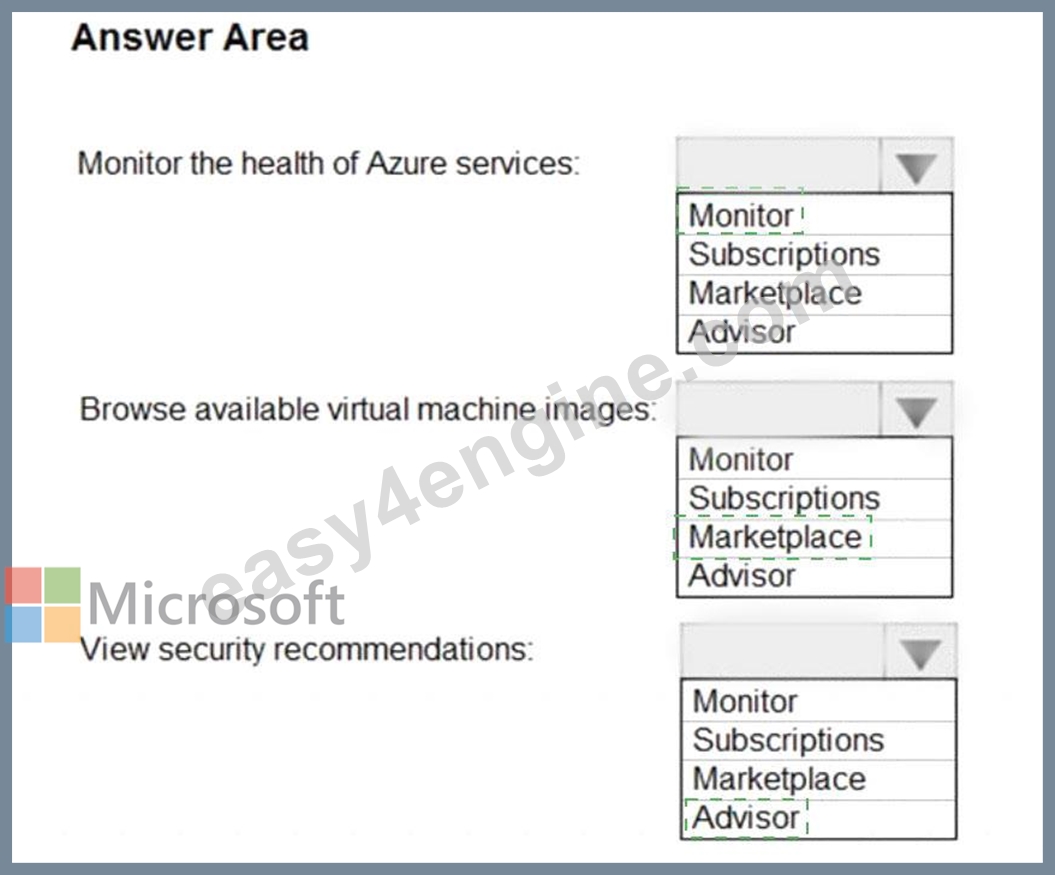
NEW QUESTION 105
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.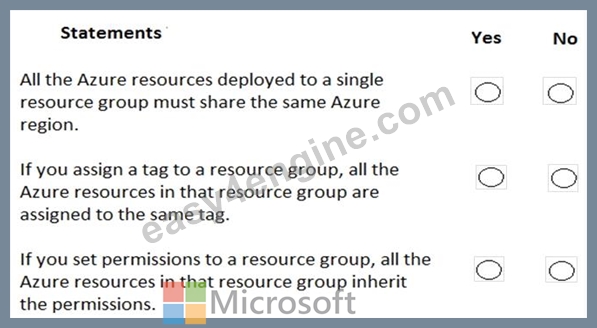
Answer:
Explanation: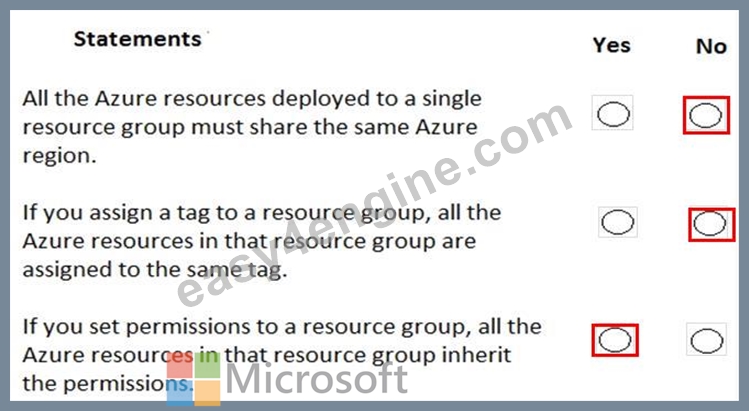
NEW QUESTION 106
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.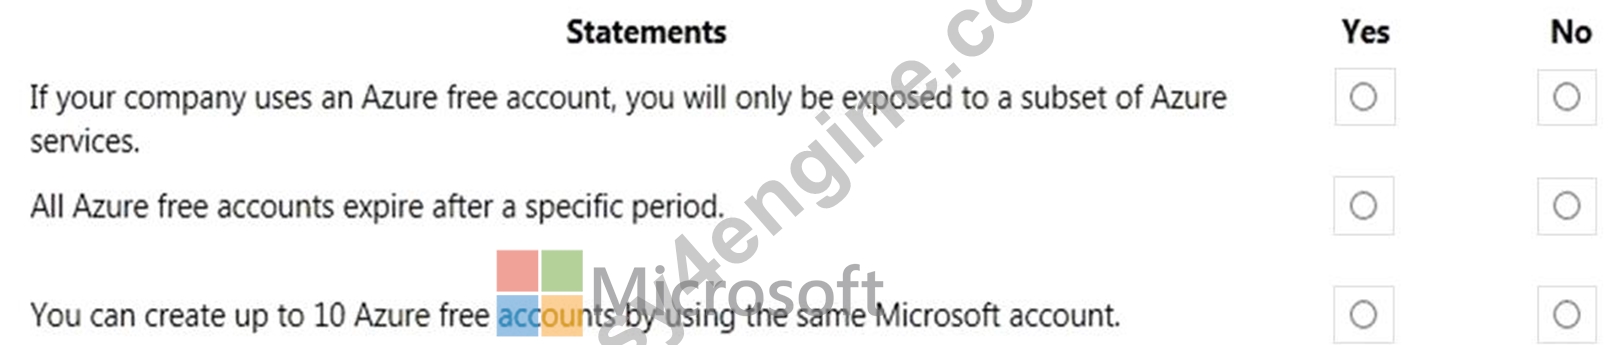
Answer:
Explanation: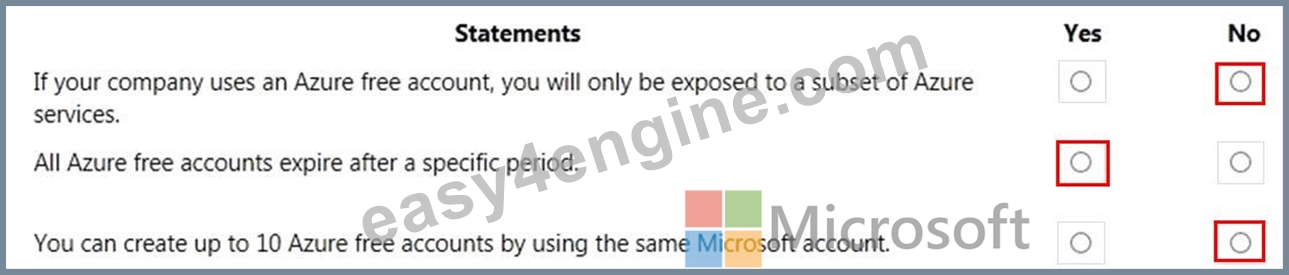
NEW QUESTION 107
You plan to extend your company's network to Azure. The network contains a VPN appliance that uses an IP address of 131.107.200.1.
You need to create an Azure resource that identifies the VPN appliance.
Which Azure resource should you create? To answer, select the appropriate resource in the answer area.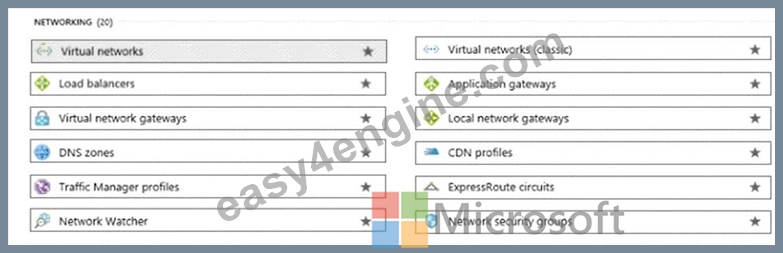
Answer:
Explanation: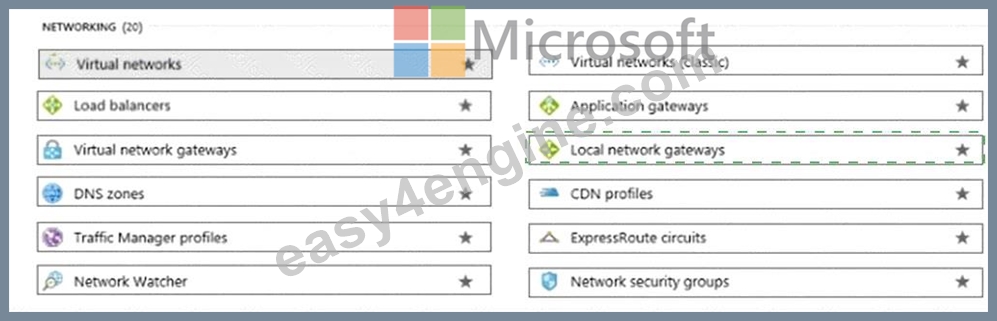
NEW QUESTION 108
Match the term to the correct definition.
Instructions: To answer, drag the appropriate term from the column on the left to its description on the right.
Each term may be used once, more than once, or not at all.
NOTE: Each correct match is worth one point.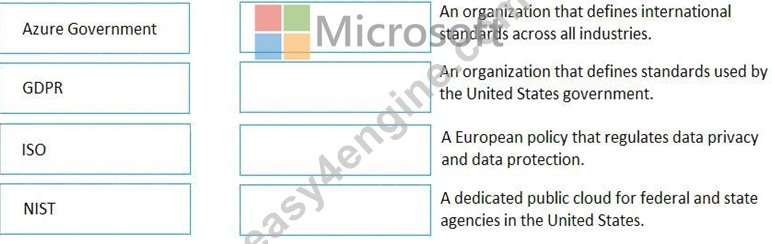
Answer:
Explanation: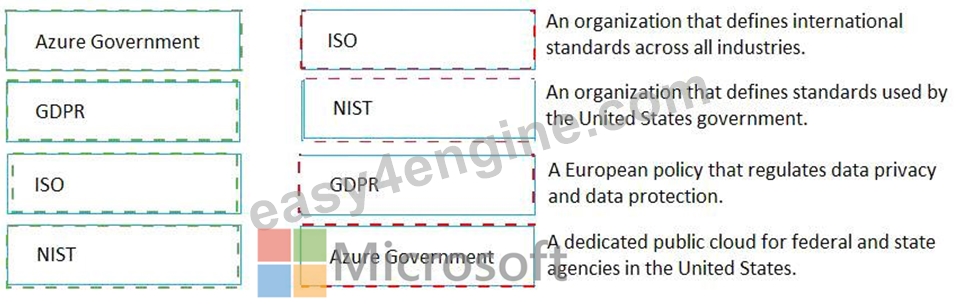
Explanation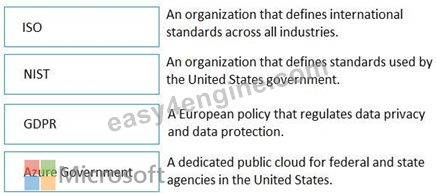
Section: Understand Security, Privacy, Compliance and Trust
NEW QUESTION 109
You have a resource group named RG1.
You plan to create virtual networks and app services in RG1.
You need to prevent the creation of virtual machines only in RG1.
What should you use?
- A. a lock
- B. an Azure role
- C. a tag
- D. an Azure policy
Answer: D
Explanation:
Section: Understand Security, Privacy, Compliance and Trust
Explanation:
Azure policies can be used to define requirements for resource properties during deployment and for already existing resources. Azure Policy controls properties such as the types or locations of resources.
Azure Policy is a service in Azure that you use to create, assign, and manage policies. These policies enforce different rules and effects over your resources, so those resources stay compliant with your corporate standards and service level agreements.
In this question, we would create a Azure policy assigned to the resource group that denies the creation of virtual machines in the resource group.
You could place a read-only lock on the resource group. However, that would prevent the creation of any resources in the resource group, not virtual machines only. Therefore, an Azure Policy is a better solution.
References:
https://docs.microsoft.com/en-us/azure/governance/policy/overview
NEW QUESTION 110
......
Verified AZ-900 Exam Dumps Q&As - Provide AZ-900 with Correct Answers: https://www.easy4engine.com/AZ-900-test-engine.html
Pass Your AZ-900 Dumps Free Latest Microsoft Practice Tests: https://drive.google.com/open?id=1Bs8rrigcfachrPWOxROhyJtt2vkNF_lm
