

Latest MS-100 Pass Guaranteed Exam Dumps with Accurate & Updated Questions
MS-100 Exam Brain Dumps - Study Notes and Theory
The MS-100 exam is intended for IT professionals who are responsible for managing Microsoft 365 services in an enterprise environment. MS-100 exam covers various topics including managing user identity and roles, managing access and authentication, implementing security and compliance, and managing Microsoft 365 services. These topics are crucial for IT professionals who want to ensure the security and reliability of Microsoft 365 services for their organization.
Microsoft MS-100 certification exam is designed for IT professionals who are responsible for managing Microsoft 365 identities and services. MS-100 exam is one of the most popular Microsoft certification exams and is highly sought after by IT professionals who want to demonstrate their expertise in managing cloud-based technologies. The MS-100 exam is a key requirement for earning the Microsoft 365 Certified: Enterprise Administrator Expert certification.
Microsoft MS-100 exam is a requirement for the Microsoft 365 Certified: Enterprise Administrator Expert certification. Microsoft 365 Identity and Services certification is intended for IT professionals who have experience in managing Microsoft 365 services and are looking to advance their career in managing enterprise-level services.
NEW QUESTION # 72
You are evaluating the use of multi-factor authentication (MFA).
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: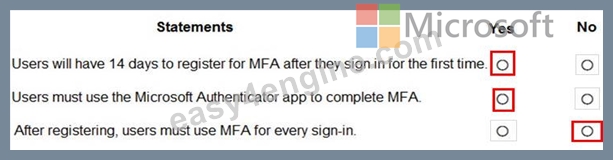
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/howto-identity-protection-configure-mfa-policy
https://blog.admindroid.com/configuring-and-managing-mfa-in-office-365/
NEW QUESTION # 73
Your network contains an Active Directory domain named contoso.com. The domain contains five domain controllers.
You purchase Microsoft 365 and plan to implement several Microsoft 365 services.
You need to identify an authentication strategy for the planned Microsoft 365 deployment. The solution must meet the following requirements:
Ensure that users can access Microsoft 365 by using their on-premises credentials.
Use the existing server infrastructure only.
Store all user passwords on-premises only.
Be highly available.
Which authentication strategy should you identify?
- A. pass-through authentication and seamless SSO with password hash synchronization
- B. federation
- C. pass-through authentication and seamless SSO
- D. password hash synchronization and seamless SSO
Answer: C
NEW QUESTION # 74
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You configure a multi-factor authentication (MFA) registration policy that has the following settings:
Assignments:
- Include: Group1
- Exclude: Group2
Access controls: Require Azure MFA registration
Enforce Policy: On
You create a conditional access policy that has the following settings:
Name: Policy1
Assignments:
- Include: Group2
- Exclude: Group1
Access controls:
- Grant, Require multi-factor authentication
Enable policy: On
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/howto-identity-protection-configure-mfa-policy
https://docs.microsoft.com/en-us/microsoft-365/admin/security-and-compliance/set-up-multi-factor-authentication?view=o365-worldwide
NEW QUESTION # 75
Your company has a Microsoft 365 subscription.
You upload several archive PST files to Microsoft 365 by using the Security & Compliance admin center.
A month later, you attempt to run an import job for the PST files.
You discover that the PST files were deleted from Microsoft 365.
What is the most likely cause of the files being deleted? More than one answer choice may achieve the goal.
Select the BEST answer.
- A. Another administrator deleted the PST files.
- B. The PST files were corrupted and deleted by Microsoft 365 security features.
- C. PST files are deleted automatically from Microsoft 365 after 30 days.
- D. The size of the PST files exceeded a storage quota and caused the files to be deleted.
Answer: C
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/faqimporting-pst-files-to-office-365
NEW QUESTION # 76
Your company has a Microsoft 365 tenant.
You plan to allow users from the engineering department to enroll their mobile device in mobile device management (MDM).
The device type restrictions are configured as shown in the following table.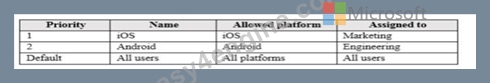
The device limit restrictions are configured as shown in the following table.
What is the effective configuration for the members of the Engineering group? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.
Answer:
Explanation: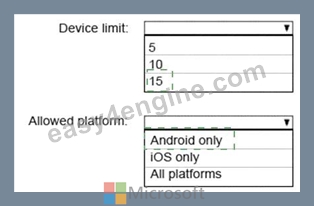
Explanation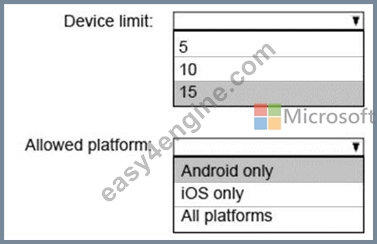
When multiple policies are applied to groups that users are a member of, only the highest priority (lowest number) policy applies.
In this case, the Engineering users are assigned two device type policies (the default policy and the priority 2 policy). The priority 2 policy has a higher priority than the default policy so the Engineers' allowed platform is Android only.
The engineers have two device limit restrictions policies applied them. The priority1 policy is a higher priority than the priority2 policy so the priority1 policy device limit (15) applies.
Reference:
https://docs.microsoft.com/en-us/intune/enrollment/enrollment-restrictions-set
NEW QUESTION # 77
Your company has a hybrid deployment of Azure Active Directory (Azure AD).
You purchase a Microsoft 365 subscription.
Your company has a hybrid deployment of Azure Active Directory (Azure AD).
You purchase a Microsoft 365 subscription.
You plan to migrate the Home folder of each user to Microsoft 365 during several weeks. Each user has a device that runs Windows 10.
You need to recommend a solution to migrate the Home folder of five administrative users as quickly as possible.
Which three actions should you recommend be performed in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order. Each user has a device that runs Windows 10.
You need to recommend a solution to migrate the Home folder of five administrative users as quickly as possible.
Which three actions should you recommend be performed in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
You need to configure a Group Policy Object (GPO) with the OneDrive settings required to redirect the Home folder of each user to Microsoft 365.
Before you can configure the Group Policy, you need to download the OneDrive Administrative Templates.
These templates add the required OneDrive settings to Group Policy so you can configure the settings as required.
After the OneDrive settings have been configured in Group Policy, you can run the gpupdate /force command on the five computers to apply the new Group Policy settings immediately.
Reference:
https://practical365.com/clients/onedrive/migrate-home-drives-to-onedrive-for-business/
NEW QUESTION # 78
You have a Microsoft 365 E5 subscription that contains an Azure Active Directory (Azure AD) tenant named contoso.com. The tenant contains a Microsoft SharePoint Online site named Site1 and the accounts shown in the following table.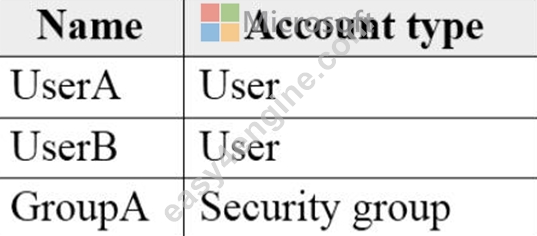
You have an on-premises server named Server1 that contains a folder named Folder1. Folder1 contains the files shown in the following table.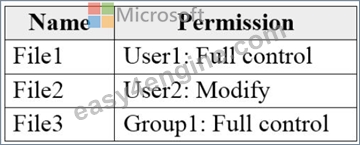
The User1, User2, and Group1 accounts have the security identifiers (SIDs) shown in the following table.
You use the SharePoint Migration Tool to migrate Folder1 to Site1. You preserve the file share permissions and use the following user mapping file.
S-1-5-21-4534338-1127018997-2609994386-1304, [email protected], FALSE
S-1-5-21-4534338-1127018997-2609994386-1228, [email protected], FALSE
S-1-5-21-4534338-1127018997-2609994386-1106, GroupA, TRUE
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point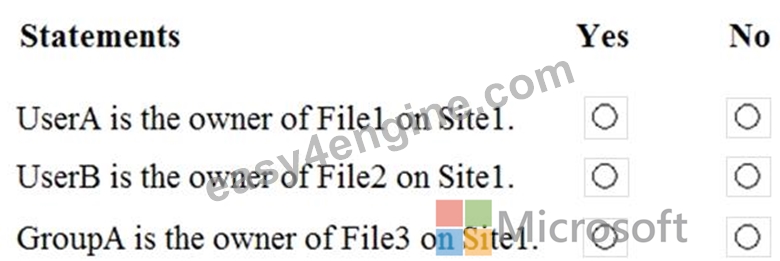
Answer:
Explanation:
NEW QUESTION # 79
You have several Microsoft SharePoint document libraries in your on-premises environment.
You have a Microsoft 365 tenant that has directory synchronization implemented.
You plan to move all the document libraries to SharePoint Online.
You need to recommend a migration strategy for the document libraries.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/sharepointmigration/how-to-use-the-sharepoint-migration-tool
NEW QUESTION # 80
You have a Microsoft 365 E5 subscription.
You need to ensure that users are prompted for multi-factor authentication (MFA) when they attempt to access Microsoft SharePoint Online resources. Users must NOT be prompted for MFA when they attempt to access other Microsoft 365 services.
What should you do?
- A. From the Cloud App Security admin center, create an app access policy.
- B. From the multi-factor authentication page, configure the users settings.
- C. From the Microsoft Endpoint Manager admin center, create an app protection policy.
- D. From the Azure Active Directory admin center, create a conditional access policy.
Answer: D
Explanation:
Section: [none]
Explanation:
Multi-factor authentication (MFA) is configured through conditional access policies.
Reference:
https://docs.microsoft.com/en-us/appcenter/general/configuring-aad-conditional-access
NEW QUESTION # 81
Your network contains an Active Directory domain and a Microsoft Azure Active Directory (Azure AD) tenant.
You implement directory synchronization for all 10.000 users in the organization.
You automate the creation of 100 new user accounts.
You need to ensure that the new user accounts synchronize to Azure AD as quickly as possible Which command should you run? To answer, select the appropriate options in the answer area.
NOTE: Each correct select ion is worth one point.
Answer:
Explanation: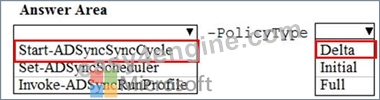
Explanation:
Azure AD Connect synchronizes Active Directory to Azure Active Directory on a schedule. The minimum time between synchronizations is 30 minutes.
If you want to synchronize changes to Active Directory without waiting for the next sync cycle, you can initiate a sync by using the Start-AdSyncSyncCycle. The Delta option synchronizes changes to Active Directory made since the last sync. The Full option synchronizes all Active Directory objects including those that have not changed.
Reference:
https://blogs.technet.microsoft.com/rmilne/2014/10/01/how-to-run-manual-dirsync-azure-active-directory-sync-updates/
NEW QUESTION # 82
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
You need to prevent users from accessing your Microsoft SharePoint Online sites unless the users are connected to your on-premises network.
Solution: From the Azure Active Directory admin center, you create a trusted location and a conditional access policy.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Conditional Access in SharePoint Online can be configured to use an IP Address white list to allow access.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/location-condition
https://techcommunity.microsoft.com/t5/Microsoft-SharePoint-Blog/Conditional-Access-in-SharePoint-Onlineand-OneDrive-for/ba-p/46678
NEW QUESTION # 83
Your network contains an Active Directory domain and a Microsoft Azure Active Directory (Azure AD) tenant.
You implement directory synchronization for all 10.000 users in the organization.
You automate the creation of 100 new user accounts.
You need to ensure that the new user accounts synchronize to Azure AD as quickly as possible Which command should you run? To answer, select the appropriate options in the answer area.
NOTE: Each correct select ion is worth one point.
Answer:
Explanation:
Explanation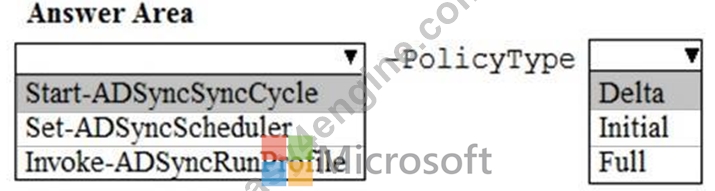
Azure AD Connect synchronizes Active Directory to Azure Active Directory on a schedule. The minimum time between synchronizations is 30 minutes.
If you want to synchronize changes to Active Directory without waiting for the next sync cycle, you can initiate a sync by using the Start-AdSyncSyncCycle. The Delta option synchronizes changes to Active Directory made since the last sync. The Full option synchronizes all Active Directory objects including those that have not changed.
Reference:
https://blogs.technet.microsoft.com/rmilne/2014/10/01/how-to-run-manual-dirsync-azure-active-directory-sync-u
NEW QUESTION # 84
You have a Microsoft 365 subscription.
You need to implement Windows Defender Advanced Threat Protection (ATP) for all the supported devices enrolled devices enrolled on mobile device management (MDM).
What should you include in the device configuration profile? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.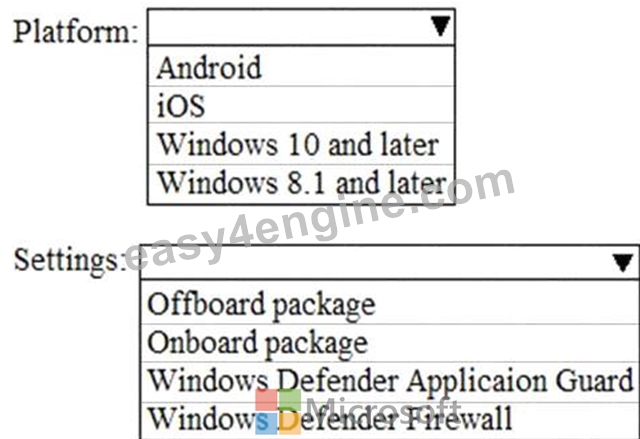
Answer:
Explanation: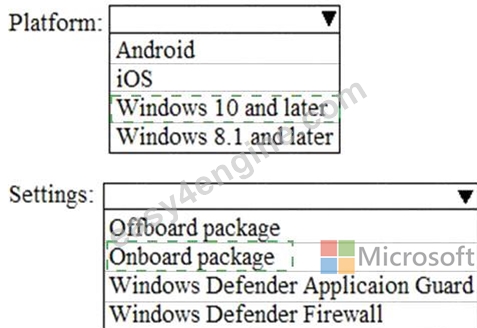
Explanation
You can integrate Microsoft Defender Advanced Threat Protection (Microsoft Defender ATP) with Microsoft Intune as a Mobile Threat Defense solution. Integration can help you prevent security breaches and limit the impact of breaches within an organization. Microsoft Defender ATP works with devices that run Windows 10 or later.
When you establish a connection from Intune to Microsoft Defender ATP, Intune receives a Microsoft Defender ATP onboarding configuration package from Microsoft Defender ATP. This package is deployed to devices by using a device configuration profile.
Reference:
https://docs.microsoft.com/en-us/intune/advanced-threat-protection
NEW QUESTION # 85
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You need to assign User2 the required roles to meet the security requirements.
Solution: From the Office 365 admin center, you assign User2 the Security Reader role. From the Exchange admin center, you assign User2 the Compliance Management role.
Does this meet the goal?
- A. NO
- B. Yes
Answer: B
Explanation:
Explanation
* User2 must be able to view reports and schedule the email delivery of security and compliance reports.
The Security Reader role can view reports.
The Compliance Management role can schedule the email delivery of security and compliance reports.
Reference:
https://docs.microsoft.com/en-us/exchange/permissions-exo/permissions-exo
NEW QUESTION # 86
You have a Microsoft Azure Active Directory (Azure AD) tenant.
Your company implements Windows Information Protection (WIP).
You need to modify which users and applications are affected by WIP.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.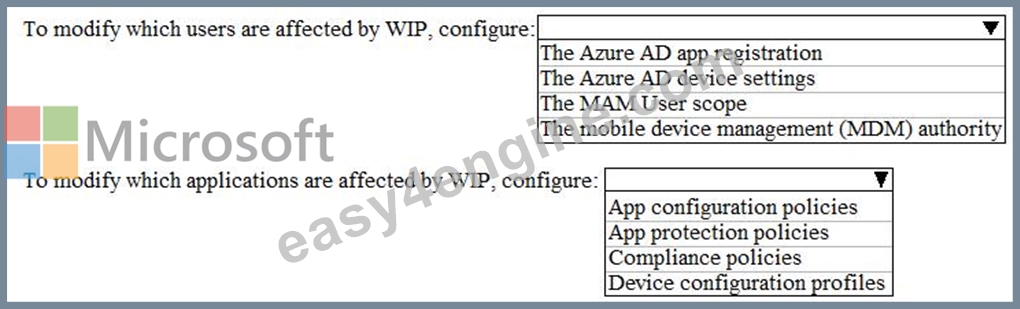
Answer:
Explanation: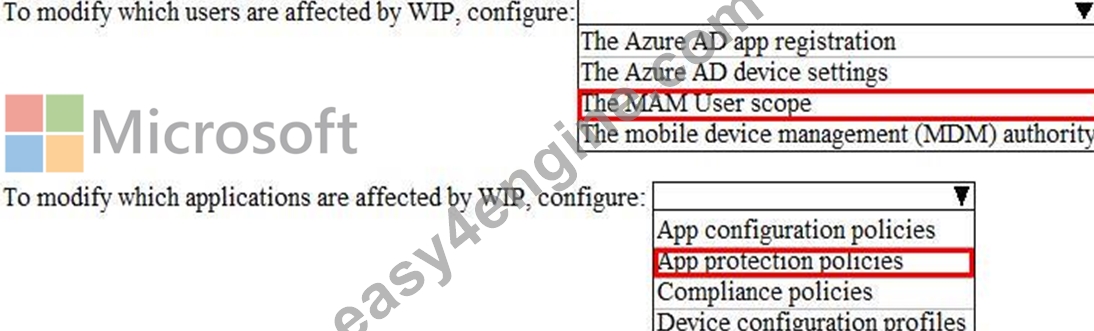
Reference:
https://docs.microsoft.com/en-us/windows/security/information-protection/windows-information-protection/create-wip-policy-using-intune-azure
NEW QUESTION # 87
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory forest.
You deploy Microsoft 365.
You plan to implement directory synchronization.
You need to recommend a security solution for the synchronized identities. The solution must meet the following requirements:
* Users must be able to authenticate successfully to Microsoft 365 services if Active Directory becomes unavailable.
* User passwords must be 10 characters or more.
Solution: Implement pass-through authentication and modify the password settings from the Default Domain Policy in Active Directory.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION # 88
You work at a company named Contoso, Ltd.
Contoso has a Microsoft 365 subscription that is configured to use the DNS domains shown in the following table.
Contoso purchases a company named Fabrikam, Inc.
Contoso plans to add the following domains to the Microsoft 365 subscription:
fabrikam.com
east.fabrikam.com
west.contoso.com
You need to ensure that the devices in the new domains can register by using Autodiscover.
How many domains should you verify, and what is the minimum number of enterpriseregistration DNS records you should add? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/enrollment/windows-enroll
NEW QUESTION # 89
You have a Microsoft 365 tenant that contains 300 users.
The users have Domestic and International Calling Plan licenses.
What is the maximum user phone numbers and toll-free service phone numbers can you acquire? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoftteams/how-many-phone-numbers-can-you-get
NEW QUESTION # 90
Your organization has an on-premises Microsoft Exchange Server 2016 organization. The organization is in the company's main office in Melbourne. The main office has a low-bandwidth connection to the Internet.
The organization contains 250 mailboxes.
You purchase a Microsoft 365 subscription and plan to migrate to Exchange Online next month.
In 12 months, you plan to increase the bandwidth available for the Internet connection.
You need to recommend the best migration strategy for the organization. The solution must minimize administrative effort.
What is the best recommendation to achieve the goal? More than one answer choice may achieve the goal. Select the BEST answer.
- A. cutover migration
- B. network upload
- C. hybrid migration
- D. staged migration
Answer: C
Explanation:
With a hybrid migration, you can migrate the mailboxes in small batches over a period of time which will help to avoid saturating the bandwidth. With the migration wizard, you can configure a migration batch to start outside office hours which would minimize bandwidth usage during office hours.
With a hybrid migration, you do not need to reconfigure Outlook to connect to the migrated mailbox. Outlook will automatically detect the new mailbox location. This reduces administrative effort.
Reference:
https://docs.microsoft.com/en-us/exchange/mailbox-migration/mailbox-migration
NEW QUESTION # 91
Your company is based in the United Kingdom (UK).
Users frequently handle data that contains Personally Identifiable Information (PII).
You create a data loss prevention (DLP) policy that applies to users inside and outside the company. The policy is configured as shown in the following exhibit.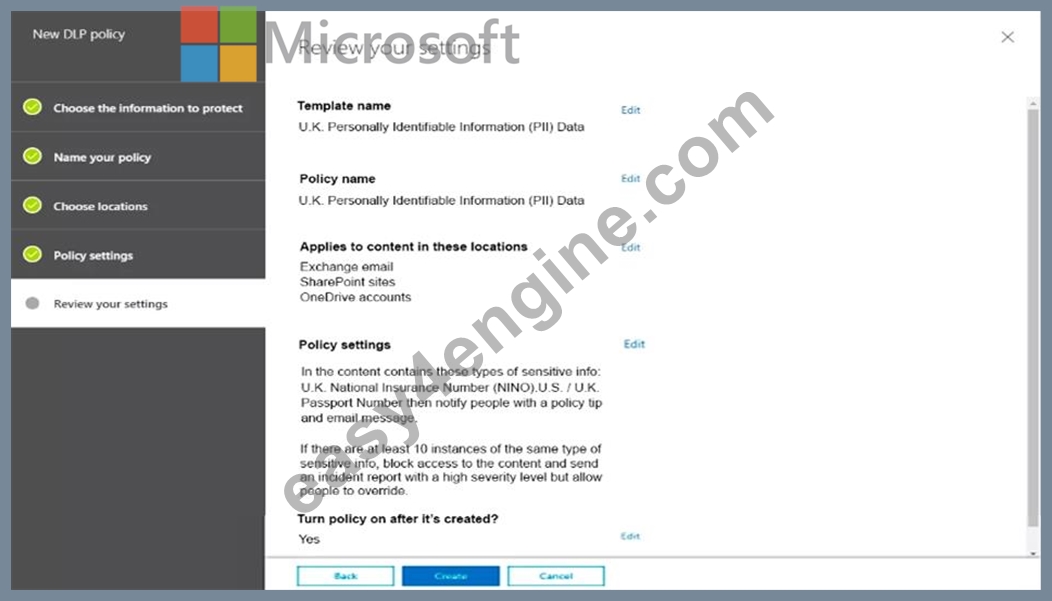
Use the drop-down menus to select the answer choice that completes each statement based in the information presented in the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
The text in the Policy Settings section of the exhibit explains what will happen.
If a user sends between 1 and 10 instances of the sensitive info (passport number), then a notification email and will be sent to the user and a policy tip will be displayed. The email will not be blocked though. Therefore, it will be allowed.
If a user sends more than 10 instances of the sensitive info (passport number), the email will be blocked and a high-severity alert generated. However, the user can override the block.
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/data-loss-prevention-policies
NEW QUESTION # 92
You implement Microsoft Azure Advanced Threat Protection (Azure ATP).
You have an Azure ATP sensor configured as shown in the following exhibit.
Updates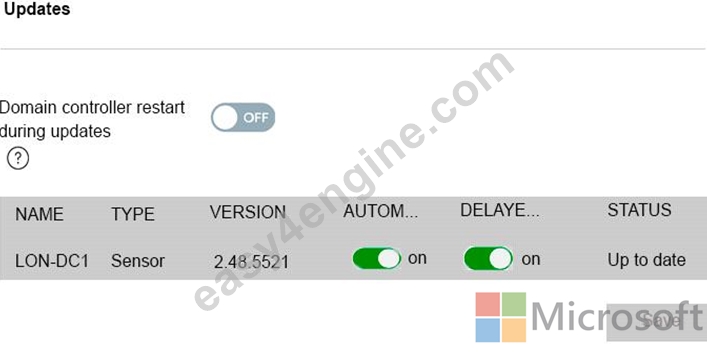
How long after the Azure ATP cloud service is updated will the sensor update?
- A. 24 hours
- B. 12 hours
- C. 7 days
- D. 1 hour
- E. 48 hours
Answer: A
Explanation:
References:
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/atp-whats-new
NEW QUESTION # 93
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an on-premises Active Directory domain named contoso.com. The domain contains the users shown in the following table.
The domain syncs to an Azure Active Directory (Azure AD) tenant named contoso.com as shown in the exhibit. (Click the Exhibit tab.)
User2 fails to authenticate to Azure AD when signing in as [email protected].
You need to ensure that User2 can access the resources in Azure AD.
Solution: From the on-premises Active Directory domain, you set the UPN suffix for User2 to @contoso.com.
You instruct User2 to sign in as [email protected].
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Explanation
The on-premises Active Directory domain is named contoso.com. You can enable users to sign on using a different UPN (different domain), by adding the domain to Microsoft 365 as a custom domain. Alternatively, you can configure the user account to use the existing domain (contoso.com).
NEW QUESTION # 94
You are developing an interactive invoicing application mat will be used by end users. The application will have the following features:
* Save invoices generated by a user to the user s OneDrive for Business.
* Email daily automated reminders.
You need to identify which permissions to grant for the application features. The solution must use the principle of least privilege. Which permission type should you grant for each feature? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.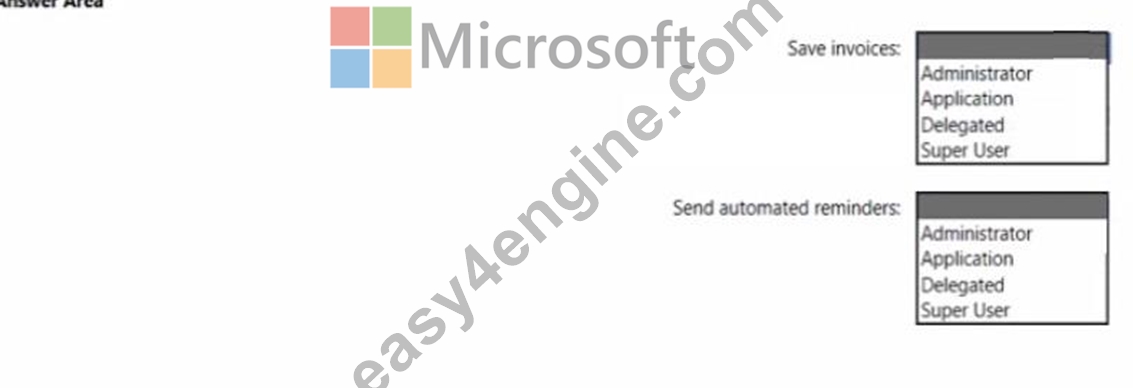
Answer:
Explanation:
NEW QUESTION # 95
You recently migrated your on-premises email solution to Microsoft Exchange Online and are evaluating which licenses to purchase.
You want the members of two groups named IT and Managers to be able to use the features shown in the following table.
The IT group contains 50 users. The Managers group contains 200 users.
You need to recommend which licenses must be purchased for the planned solution. The solution must minimize licensing costs.
Which licenses should you recommend?
- A. 200 Microsoft 365 E3 and 50 Microsoft 365 E5
- B. 250 Microsoft 365 E5 only
- C. 250 Microsoft 365 E3 only
- D. 50 Microsoft 365 E3 and 200 Microsoft 365 E5
Answer: A
NEW QUESTION # 96
......
Pass Microsoft MS-100 Test Practice Test Questions Exam Dumps: https://www.easy4engine.com/MS-100-test-engine.html
The Best Microsoft 365 Study Guide for the MS-100 Exam: https://drive.google.com/open?id=1veDymk30qZ1D7C9ba7Q48kRSIamUGCqw
