

MS-100 Dumps PDF - MS-100 Real Exam Questions Answers
Get Started: MS-100 Exam [2021] Dumps Microsoft PDF Questions
NEW QUESTION 47
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.
User1 is the owner of Group1, User2 is the owner of Group2.
You create an access review that contains the following configurations:
* Users to review, Member of a group
* Scope Everyone
* Group: Group1 and Group2
* Review Group owners
For each of the following statements, select Yes if the statement is true. Otherwise select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
References:
https://docs.microsoft.com/en-us/azure/active-directory/governance/create-access-review
NEW QUESTION 48
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an on-premises Active Directory forest named contoso.com. The forest contains the following domains:
* Contoso.com
* East.contoso.com
An Azure AD Connect server is deployed to contoso.com. Azure AD Connect syncs to an Azure Active Directory (Azure AD) tenant.
You deploy a new domain named west.contoso.com to the forest.
You need to ensure that west.contoso.com syncs to the Azure AD tenant.
Solution: From the Azure AD Connect server in contoso.com, you return the setup wizard and include the west.contoso.com domain.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Section: [none]
NEW QUESTION 49
You are evaluating the required processes for Project1.
You need to recommend which DNS record must be created before you begin the project.
Which DNS record should you recommend?
- A. alias (CNAME)
- B. host (A)
- C. host (AAA)
- D. mail exchanger (MX)
Answer: D
Explanation:
Topic 1, Fabrikam, Inc
Existing Environment
Active Directory Environment
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication.
Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as a DNS server.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements
Planned Changes
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
Project2: After the successful completion of Project1, Microsoft Teams & Skype for Business will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements
Fabrikam identifies the following technical requirements:
All users must be able to exchange email messages successfully during Project1 by using their current email address.
Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
A user named User1 must be able to view all DLP reports from the Microsoft 365 admin center.
Microsoft Office 365 ProPlus applications must be installed from a network share only.
Disruptions to email address must be minimized.
Application Requirements
Fabrikam identifies the following application requirements:
An on-premises web application named App1 must allow users to complete their expense reports online.
The installation of feature updates for Office 365 ProPlus must be minimized.
Security Requirements
Fabrikam identifies the following security requirements:
After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
The memberships of UserLicenses must be validated monthly. Unused user accounts must be removed from the group automatically.
After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
The principle of least privilege must be used.
NEW QUESTION 50
You create a Microsoft 365 Enterprise subscription.
You assign licenses for all products to all users.
You need to ensure that all Microsoft Office 365 ProPlus installations occur from a network share. The solution must prevent the users from installing Office 365 ProPlus from the Internet.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. From the Microsoft 365 admin center, configure the Software download settings.
- B. Create an XML download file.
- C. From the Microsoft 365 admin center, deactivate the Office 365 licenses for all the users.
- D. From your computer, run setup.exe /download downloadconfig.xml.
- E. From each client computer, run setup.exe /configure installconfig.xml.
Answer: A,B,E
Explanation:
You can use the Office Deployment Tool (ODT) to download the installation files for Office 365 ProPlus from a local source on your network instead of from the Office Content Delivery Network (CDN).
The first step is to create the configuration file. You can download an XML template file and modify that.
The next step to install Office 365 ProPlus is to run the ODT executable in configure mode with a reference to the configuration file you just saved. In the following example, the configuration file is named installconfig.xml. setup.exe /configure installconfig.xml After running the command, you should see the Office installation start.
To prevent the users from installing Office 365 ProPlus from the Internet, you need to configure the Software download settings (disallow downloads) in the Microsoft 365 admin center.
Reference:
https://docs.microsoft.com/en-us/deployoffice/overview-of-the-office-2016-deployment-tool#download-the-installation-files-for-office-365-proplus-from-a-local-source
NEW QUESTION 51
You have a Microsoft Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.
Your company uses Windows Defender Advanced Threat Protection (ATP). Windows Defender ATP contains the roles shown in the following table.
Windows Defender ATP contains the device groups shown in the following table.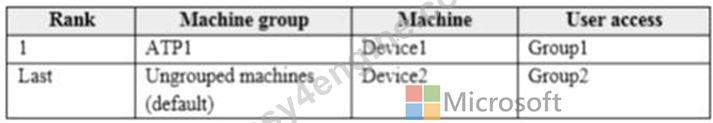
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1:
Yes. User1 is in Group1 which is assigned to Role1. Device1 is in the device group named ATP1 which Group1 has access to. Role1 gives Group1 (and User1) View Data Permission. This is enough to view Device1 in Windows Security Center.
Box 2:
Yes. User2 is in Group2 which is assigned to Role2. Role2 gives Group2 (and User2) View Data Permission. This is enough to sign in to Windows Security Center.
Box 3:
Yes. User3 is in Group3 which is assigned the Windows ATP Administrator role. Someone with a Microsoft Defender ATP Global administrator role has unrestricted access to all machines, regardless of their machine group association and the Azure AD user groups assignments.
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/user-roles
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/rbac
NEW QUESTION 52
You have a Microsoft 365 subscription.
You need to prevent phishing email messages from being delivered to your organization.
What should you do?
- A. From Security & Compliance, create a new threat management policy.
- B. From the Exchange admin center, create a spam filter policy.
- C. From the Exchange admin center, create an anti-malware policy.
- D. From Security & Compliance, create a DLP policy.
Answer: A
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/set-up-anti-phishing-policies
NEW QUESTION 53
You create a Microsoft 365 subscription.
You plan to deploy Microsoft Office 365 ProPlus applications to all the client computers at your company.
You prepare the following XML file for the planned deployment.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.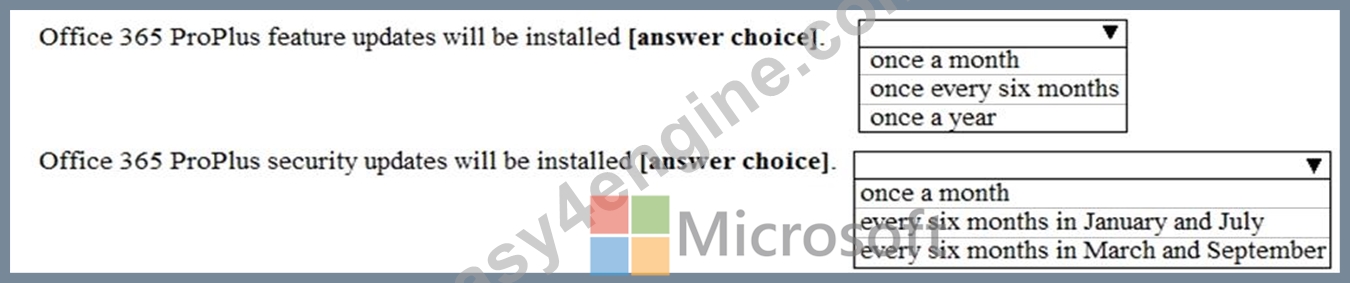
Answer:
Explanation: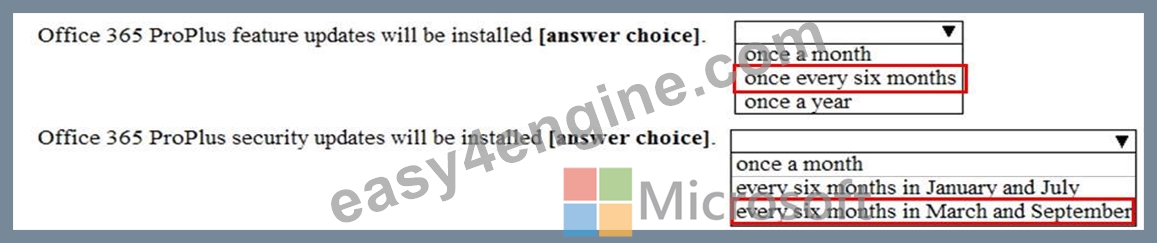
Explanation:
References:
https://docs.microsoft.com/en-us/deployoffice/configuration-options-for-the-office-2016-deployment-tool
https://docs.microsoft.com/en-us/deployoffice/overview-of-update-channels-for-office-365-proplus
NEW QUESTION 54
You have a Microsoft 365 Enterprise E5 subscription.
You add a cloud-based app named App1 to the Microsoft Azure Active Directory (Azure AD) enterprise applications list.
You need to ensure that two-step verification is enforced for all user accounts the next time they connect to App1.
Which three settings should you configure from the policy? To answer, select the appropriate settings in the answer area.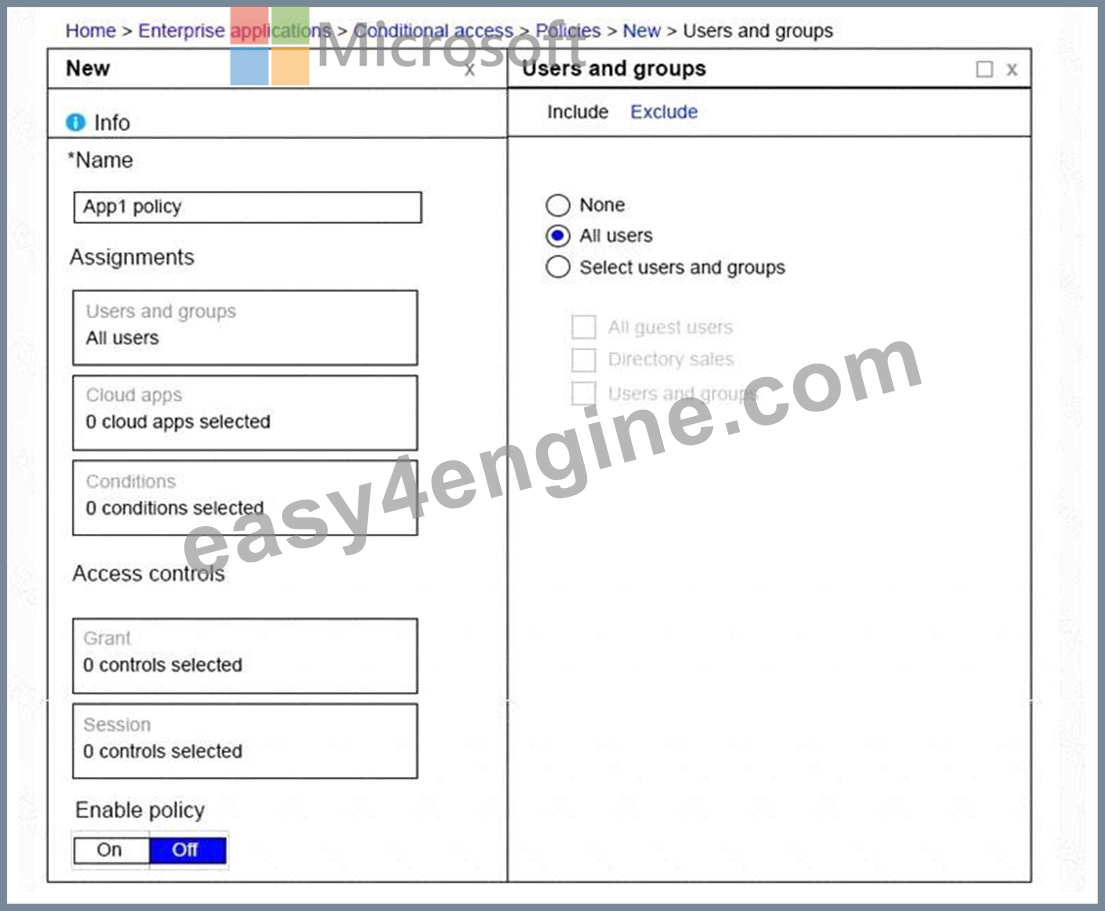
Answer:
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/best-practices
https://techcommunity.microsoft.com/t5/Enterprise-Mobility-Security/Conditional-Access-now-in-the-new-Azur
NEW QUESTION 55
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may have more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
You may now click next to proceed to the lab.
Lab information
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username: [email protected]
Microsoft 365 Password: x?-ofP?fG70o
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 11325860
You need to ensure that an external user named [email protected] can register an application in your Microsoft 365 tenant. The solution must use the principle of least privilege.
To answer, sign in to the Microsoft 365 portal.
Answer:
Explanation:
See explanation below.
Explanation
You need to create a guest account for the external user and assign the Application Developer role. As the user's domain is an external domain, you will need to 'invite' the user. The external user will need to accept the invitation to create the account.
1. Go to the Azure Active Directory Admin Center.
2. In the left navigation pane, select Users.
3. Click on the '+ New Guest User' link.
4. Ensure that the 'Invite user' option is selected.
5. Enter [email protected] in the email address field.
6. In the Roles section, 'user' will be selected by default. Click on 'user' to open a list of roles.
7. Select Application Developer in the list and click the 'Select' button to assign the role.
8. Click the 'Invite' button to send the invitation.
NEW QUESTION 56
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory domain.
You deploy a Microsoft Azure Active Directory (Azure AD) tenant.
Another administrator configures the domain to synchronize to Azure AD.
You discover that 10 user accounts in an organizational unit (OU) are NOT synchronized to Azure AD. All the other user accounts synchronized successfully.
You review Azure AD Connect Health and discover that all the user account synchronizations completed successfully.
You need to ensure that the 10 user accounts are synchronized to Azure AD.
Solution: You run idfix.exeand export the 10 user accounts.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Section: [none]
Explanation:
The question states that "all the user account synchronizations completed successfully". If there were problems with the 10 accounts that needed fixing with idfix.exe, there would have been synchronization errors in Azure AD Connect Health.
It is likely that the 10 user accounts are being excluded from the synchronization cycle by a filtering rule.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-sync-configure-filtering
NEW QUESTION 57
Note: This question is part of a series of questions that present the same scenario. Each question
in the series contains a unique solution that might meet the stated goals. Some question sets
might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these
questions will not appear in the review screen.
Your company has a Microsoft Office 365 tenant.
You suspect that several Office 365 features were recently updated.
You need to view a list of the features that were recently updated in the tenant.
Solution: You use Dashboard in Security & Compliance.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION 58
Your Network contains an on-premises Active Directory domain named contoso.local. The domain contains five domain controllers.
Your company purchases Microsoft 365 and creates a Microsoft Anne Active Directory (Azure AD) tenant named .contoso.onmicrosoft.com.
You plan to implement pass- through authentication.
You need to prepare the environment for the planned implementation of pass-through authentication.
Which three actions should you perform? Each correct answer presents pan of the solution.
NOTE: Each correct selection is worth one point.
- A. From Active Directory Domains and Trusts, add a UPN suffix.
- B. Modify the User logon name for each user account.
- C. Modify the email address attribute for each user account.
- D. From a domain controller, install an authentication Agent.
- E. From the Azure portal, add a custom domain name.
- F. From the Azure portal, configure an authentication method.
Answer: A,D,E
Explanation:
To implement pass-through authentication, you need to install and configure Azure AD Connect.
The on-premise Active Directory domain is named contoso.local. Before you can configure Azure AD Connect, you need to purchase a routable domain, for example, contoso.com.
You then need to add the domain contoso.com to Microsoft as a custom domain name.
The user accounts in the Active Directory domain need to be configured to use the domain name contoso.com as a UPN suffix. You need to add contoso.com to the Active Directory first by using Active Directory Domains and Trusts to add contoso.com add a UPN suffix. You can then configure each account to use the new UPN suffix.
An Authentication Agent is required on a domain controller to perform the authentication when pass-through authentication is used. When the custom domain and user accounts are configured, you can install and configure Azure AD Connect. An Authentication Agent is installed when you select the pass-through authentication option in the Azure AD Connect configuration or you can install the Authentication Agent manually.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-pta-quick-start
NEW QUESTION 59
Your network contains an on-premises Active Directory forest named contoso.com. The forest contains the following domains:
Contoso.com
East.contoso.com
The forest contains the users shown in the following table.
The forest syncs to an Azure Active Directory (Azure AD) tenant named contoso.com as shown in the exhibit. (Click the Exhibit tab.)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 60
You have a Microsoft 365 tenant that contains Microsoft Exchange Online.
You plan to enable calendar sharing with a partner organization named adatum.com. The partner organization also has a Microsoft 365 tenant.
You need to ensure that the calendar of every user is available to the users in adatum.com immediately.
What should you do?
- A. From the Microsoft 365 admin center, modify the Organization profile settings.
- B. From the Exchange admin center, create a sharing policy.
- C. From the Exchange admin center, create a new organization relationship
- D. From the Microsoft 365 admin center, configure external site sharing.
Answer: C
Explanation:
References:
https://docs.microsoft.com/en-us/exchange/sHYPERLINK "https://docs.microsoft.com/en-us/exchange/sharing/organization-relationships/create-an-organization-relationship"haring/organization-relationships/create-an-organization-relationship
NEW QUESTION 61
Your network contains an Active Directory domain named contoso.com. The domain contains five domain controllers.
You purchase Microsoft 365 and plan to implement several Microsoft 365 services.
You need to identify an authentication strategy for the planned Microsoft 365 deployment. The solution must meet the following requirements:
* Ensure that users can access Microsoft 365 by using their on-premises credentials.
* Use the existing server infrastructure only.
* Store all user passwords on-premises only.
* Be highly available.
Which authentication strategy should you identify?
- A. pass-through authentication and seamless SSO with password hash synchronization
- B. pass-through authentication and seamless SSO
- C. password hash synchronization and seamless SSO
- D. federation
Answer: B
NEW QUESTION 62
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may have more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
You may now click next to proceed to the lab.
Lab information
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
[email protected]
Microsoft 365 Password: oL9z0=?Nq@ox
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 11098651
You need to ensure that all the users in your organization are prompted to change their password every 180 days.
To answer the question, sign in to the Microsoft 365 portal.
Answer:
Explanation:
You need to configure the Password Expiration Policy.
1. Sign in to the Microsoft 365 Admin Center.
2. In the left navigation pane, expand the Settings section then select the Settings option.
3. Click on Security and Privacy.
4. Select the Password Expiration Policy.
5. Ensure that the checkbox labelled "Set user passwords to expire after a number of days" is ticked.
6. Enter 180 in the "Days before passwords expire" field.
7. Click the 'Save changes' button.
NEW QUESTION 63
......
What Are The Pre-requisite for The Exam?
As we have already told that MS-100 leads to an expert-level certification, one must know about great prior expertise required. The vendor suggests owning any of the below-mentioned certificates before taking up the Microsoft MS-100 test:
- Microsoft 365 Certified: Security Administrator Associate
- Microsoft 365 Certified: Modern Desktop Administrator Associate
- Microsoft 365 Certified: Teams Administrator Associate
- MCSE: Productivity Solutions Expert
- Microsoft 365 Certified: Messaging Administrator Associate
Key Details (Exam Pattern)
Microsoft doesn’t reveal the details of its certification tests. However, you can expect about 40-60 questions in your exam delivery that you will need to complete within 180 minutes. There is no denying that you will be pressed for time during this test, so you should answer the questions quickly if you want to complete all of them in time.
The MS-100 certification exam is available in the English and Japanese languages. To schedule the session, you will need to pay $165. This is the price applicable to the United States. If you live in another country, the cost is likely to be lower. Check out the official webpage to know the exact sum of the fee depending on your location.
There are many resources that you can use to study for the Microsoft MS-100 test. First of all, pay attention to the instructor-led training course “Microsoft 365 Identity and Services” offered on the certification exam webpage. This will equip you with the knowledge and skills required to get certified. It is also recommended that you use practice tests and exam dumps from other learning platforms.
MS-100 Premium Exam Engine pdf Download: https://www.easy4engine.com/MS-100-test-engine.html
Verified MS-100 Bundle Real Exam Dumps PDF: https://drive.google.com/open?id=1XFQqE9L-BDGgbNDJVxjkAq1dZovFnMWH
